How to Run JavaScript on Any Web Page with a Browser API
Learn three practical ways to run JavaScript on an open web page: DevTools, bookmarklets, and browser extensions, with security limits and code.

Short answer: use the developer-tools console for a one-off experiment, a javascript: bookmarklet for a small user-triggered action, and an extension’s scripting or content-script API for repeatable automation. None of these methods is guaranteed to work on every page. Content Security Policy (CSP), permissions, same-origin rules, browser support, frames, and the page’s own JavaScript can prevent execution.
This guide explains each route, gives runnable examples, and shows how to choose between them. The examples target a page that is already open in a desktop browser. Mobile browsers generally provide fewer scripting and extension options.
1. Choose the right browser API route
| Route | Best for | Repeatability | Main limitation |
|---|---|---|---|
| Developer tools console or saved snippet | Inspecting a page, debugging, trying a short script | Manual; snippets can be reused | Requires a developer-tools session and a user action |
| Bookmarklet | A small action you trigger on the current tab | Easy to save and reuse | CSP may block it; arbitrary code has security risks |
| Extension scripting/content script | Repeatable behavior, URL matching, packaged tools | High; can run on matching pages | Requires declared permissions and browser-specific APIs |
Ask these questions before writing code:

- Does the script run once, or on many pages?
- Must it run only after a deliberate user gesture?
- Is the code short enough to keep in a bookmark, or does it need files, tests, and settings?
- Which sites should it access?
- Will CSP, an iframe, a login boundary, or a cross-origin request affect it?
- Which browser and extension manifest version must be supported?
2. Run JavaScript interactively with developer tools
The console is the fastest way to examine and modify the currently displayed document. Use it for experiments such as finding elements, checking computed styles, or proving that a selector works before turning the code into a bookmarklet or extension.
Keep the workflow browser-neutral because console and snippet controls vary between browser versions:
- Open the browser’s developer tools for the page.
- Select the JavaScript console or a saved-snippet feature.
- Paste a small script, review it, and run it in the page context.
- Inspect the return value and the DOM, then reload the page to undo temporary changes.
// Highlight every link on the current page
for (const link of document.querySelectorAll('a')) {
  link.style.outline = '2px solid #f00';
}

// Read the first heading
const heading = document.querySelector('h1, h2');
console.log(heading?.textContent.trim());
A console script has the same page security boundaries as other page JavaScript. It cannot magically read data from another origin, bypass a login, or access browser secrets. The same-origin policy prevents a malicious site from reading a third-party webmail service where you are signed in (MDN same-origin policy).
Use a self-contained function for repeatable experiments
(() => {
  const cards = [...document.querySelectorAll('[data-card]')];
  return cards.map(card => ({
    title: card.querySelector('h2')?.textContent.trim() ?? null,
    href: card.querySelector('a')?.href ?? null
  }));
})();
Returning structured data makes it easier to inspect results without changing the page. If the page is a single-page application, wait until the relevant view has rendered before querying it.
3. Build a bookmarklet with a javascript: URL
A bookmarklet is a bookmark whose URL starts with javascript:. Activating it runs the code against the current page. MDN documents this scheme but warns: “Using javascript: URLs on the web is discouraged as it may lead to execution of arbitrary code” (MDN: javascript: URLs). Only save code you understand, and inspect bookmarklet source before clicking it.
A minimal bookmarklet
javascript:(() => {
  document.body.style.outline = '6px solid #ff3b30';
})();
Create a new bookmark, set its name, and paste the complete line into its URL field. When activated on a page, it draws an outline around the document.
Write bookmarklets that do not navigate away
The completion value of a javascript: expression matters. If the expression returns a string, the browser can treat that string as a new document. Wrap the call in an immediately invoked function and use void when appropriate:
javascript:void (() => {
  const badge = document.createElement('div');
  badge.textContent = 'Marked';
  badge.style.cssText = 'position:fixed;top:1rem;right:1rem;z-index:2147483647;background:#111;color:#fff;padding:.5rem;border-radius:.25rem';
  document.body.appendChild(badge);
})();
MDN specifically recommends prefixing a function call with void when you need to avoid accidental navigation caused by a returned string.
Bookmarklet limitations and CSP
- A page’s Content Security Policy can block inline JavaScript, including
javascript:navigation. A policy withdefault-srcorscript-srcand no suitable allowance may prevent execution (MDN CSP reference). - Browser behavior for
javascript:URLs can differ, and individual sites have different policies. - Code runs in the current document, not automatically in every iframe or tab.
- Long scripts become difficult to review and maintain. Minification also makes security review harder.
4. Inject code with a browser extension
For repeated behavior, build an extension. Chrome’s chrome.scripting API executes scripts in different contexts and is available for Manifest V3 in Chrome 88 and later (Chrome scripting API). Chrome requires the scripting permission plus host permissions or the temporary activeTab permission. MDN documents equivalent WebExtension scripting calls and notes that browser support differs (MDN scripting API).
Complete Chrome Manifest V3 example
This small extension adds a button to the toolbar. When clicked, it injects a function into the active tab and outlines headings.
// manifest.json
{
  "manifest_version": 3,
  "name": "Outline headings",
  "version": "1.0.0",
  "action": { "default_title": "Outline headings" },
  "permissions": ["scripting", "activeTab"],
  "background": { "service_worker": "service-worker.js" }
}
// service-worker.js
chrome.action.onClicked.addListener(async (tab) => {
if (!tab.id) return;
await chrome.scripting.executeScript({
target: { tabId: tab.id },
func: () => {
for (const heading of document.querySelectorAll('h1, h2, h3')) {
heading.style.outline = '2px solid #0a84ff';
}
}
});
});Load the folder as an unpacked extension in the browser’s extension development area, then click the action while viewing a page. The activeTab permission grants temporary access after the user invokes the extension. Use persistent host permissions only when the product genuinely needs automatic access to known sites.
Inject a file and register content scripts
await chrome.scripting.executeScript({
  target: { tabId: tab.id, allFrames: true },
  files: ['content.js']
});
// content.js
const panel = document.querySelector('[data-debug-panel]');
if (panel) panel.remove();
allFrames includes accessible frames, but cross-origin frames and restricted browser pages still impose limits. For behavior that should run whenever a matching URL loads, declare a content script in the manifest or use the dynamic registration API documented by MDN.
Permissions, origins, and isolated worlds
- Declare only the permissions you need. Host permissions determine which pages the extension may access.
- Use
activeTabfor a user-triggered, temporary action when persistent access is unnecessary. - Page scripts and extension code can have different JavaScript worlds. Passing data between them requires an explicit, carefully validated bridge.
- Extension access does not remove the same-origin policy for network requests. Browser API support and permission behavior vary across Chrome, Firefox, Edge, and other browsers (MDN WebExtensions APIs).
5. Practical patterns for real pages
Wait for dynamic content
const waitFor = (selector, timeout = 10000) => new Promise((resolve, reject) => {
  const existing = document.querySelector(selector);
  if (existing) return resolve(existing);
  const observer = new MutationObserver(() => {
    const found = document.querySelector(selector);
    if (found) { observer.disconnect(); resolve(found); }
  });
  observer.observe(document.documentElement, { childList: true, subtree: true });
  setTimeout(() => { observer.disconnect(); reject(new Error(`Timed out: ${selector}`)); }, timeout);
});

waitFor('[data-results]').then((node) => {
  node.style.background = 'yellow';
}).catch(console.error);
Handle shadow DOM and iframes
querySelectorAll does not cross a shadow root. If a component exposes an open root, query it explicitly. Closed roots cannot be inspected through ordinary page JavaScript. An iframe has its own document; same-origin frames can be accessed through frame.contentDocument, while cross-origin frames cannot be read by page code.
Make scripts reversible
const marker = 'data-my-script-outline';
for (const el of document.querySelectorAll('button')) {
  el.setAttribute(marker, '1');
  el.style.outline = '2px solid orange';
}
// Later: document.querySelectorAll(`[${marker}]`).forEach(el => { el.style.outline = ''; el.removeAttribute(marker); });
6. Troubleshooting
| Symptom | Likely cause | Fix |
|---|---|---|
| Bookmarklet does nothing | CSP blocks javascript: navigation |
Use the console or an extension with the required permission; inspect the page’s CSP. |
| Page changes to plain text | The script returned a string | Wrap the code in void (() => { ... })(). |
Cannot access contents of url |
Missing host permission, inactive tab permission, or a restricted browser page | Add the narrow permission you need, trigger activeTab from a user action, and test on a normal HTTP(S) page. |
Selector returns null |
SPA content has not rendered, selector is wrong, or element is inside a shadow root | Wait with a MutationObserver, verify the selector, or query an open shadow root. |
| Works in the console but not in an extension | Different execution world or missing permission | Declare scripting and page access, then pass data through an explicit bridge. |
| Network request fails | Same-origin or CORS restrictions | Run the request from an extension context with the correct host permission, or use a server-side API. |
| Only the top page changes | Target was not configured for frames | Use allFrames: true where permitted and handle each frame separately. |
7. Performance, reliability, and security
- Keep DOM work bounded. Prefer one scoped query over repeatedly scanning
document. Batch style changes with a class and one stylesheet update. - Throttle observers. Mutation observers on large applications can fire thousands of times. Disconnect them after the target appears and debounce expensive processing.
- Plan for navigation. Single-page apps replace content without a full reload. Re-run initialization on route changes or observe a stable root.
- Fail safely. Set timeouts, catch rejected promises, and avoid destructive writes. Record whether a script ran so users can undo it.
- Review code before running it. A bookmarklet or extension can read and modify anything its permissions allow. Never paste an unknown script into a signed-in page.
- Respect permissions. Same-origin policy, CSP, extension permissions, and browser-specific restrictions are security boundaries, not bugs to bypass.
8. Or skip the browser setup
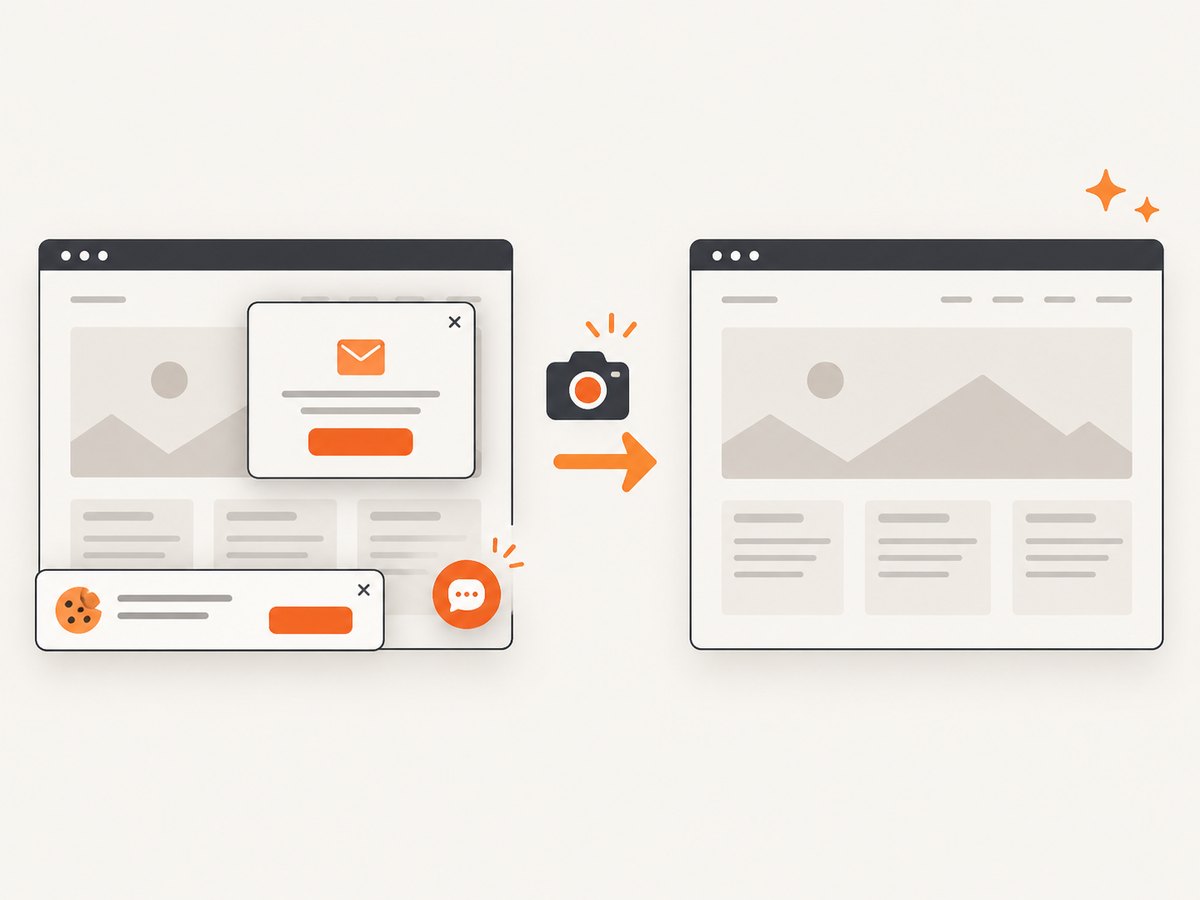
If your goal is to capture the result of a page after JavaScript renders, ScreenshotNeo provides a website screenshot API and MCP server. It can run a capture without you packaging a bookmarklet or extension:
curl -G "https://api.screenshotneo.com/v1/shot" -d access_key=YOUR_API_KEY --data-urlencode url=https://stripe.com -o shot.webpimport requests
r = requests.get("https://api.screenshotneo.com/v1/shot", params={"access_key": "YOUR_API_KEY", "url": "https://stripe.com"}, timeout=90)
open("shot.webp", "wb").write(r.content)const q = new URLSearchParams({ access_key: 'YOUR_API_KEY', url: 'https://stripe.com' });
const res = await fetch(`https://api.screenshotneo.com/v1/shot?${q}`);See the ScreenshotNeo API documentation for request options. Cookie banners, newsletter popups, and chat widgets are removed before the shot; bot checks, blank pages, timeouts, failed loads, and cache hits are never billed, with the result identified by X-Page-Verdict and X-Billed headers. An MCP server lets AI agents use take_screenshot, get_page_info, and capture_pdf. The Free plan includes 1,000 screenshots each month with no card, and paid plans start at $5 for 3,000 shots. Create a free ScreenshotNeo account.
9. Frequently asked questions
Can JavaScript run on literally any web page?
No. CSP, restricted browser URLs, cross-origin frames, missing extension permissions, and browser differences can block execution.
Is a bookmarklet safer than an extension?
Neither is automatically safe. A bookmarklet has less setup but can run arbitrary code when clicked. An extension is reviewable and permission-scoped, but it may have broader ongoing access.
Can page JavaScript read another website’s cookies?
No. Same-origin rules and cookie protections prevent ordinary page scripts from reading another origin’s data.
When should I choose an extension?
Choose one when the behavior must run repeatedly, match selected URL patterns, interact with browser actions, or be distributed to other users.
How do I capture a page after its JavaScript finishes?
Wait for a stable selector or network state in your own browser automation, or use ScreenshotNeo’s capture options and clean-page processing to produce a screenshot or PDF without maintaining browser infrastructure.