SAST vs. DAST: Which Is Better for Application Security Testing?
SAST finds risky code early; DAST tests deployed behavior. Learn when to use each, how to combine them in CI/CD, and what both miss.
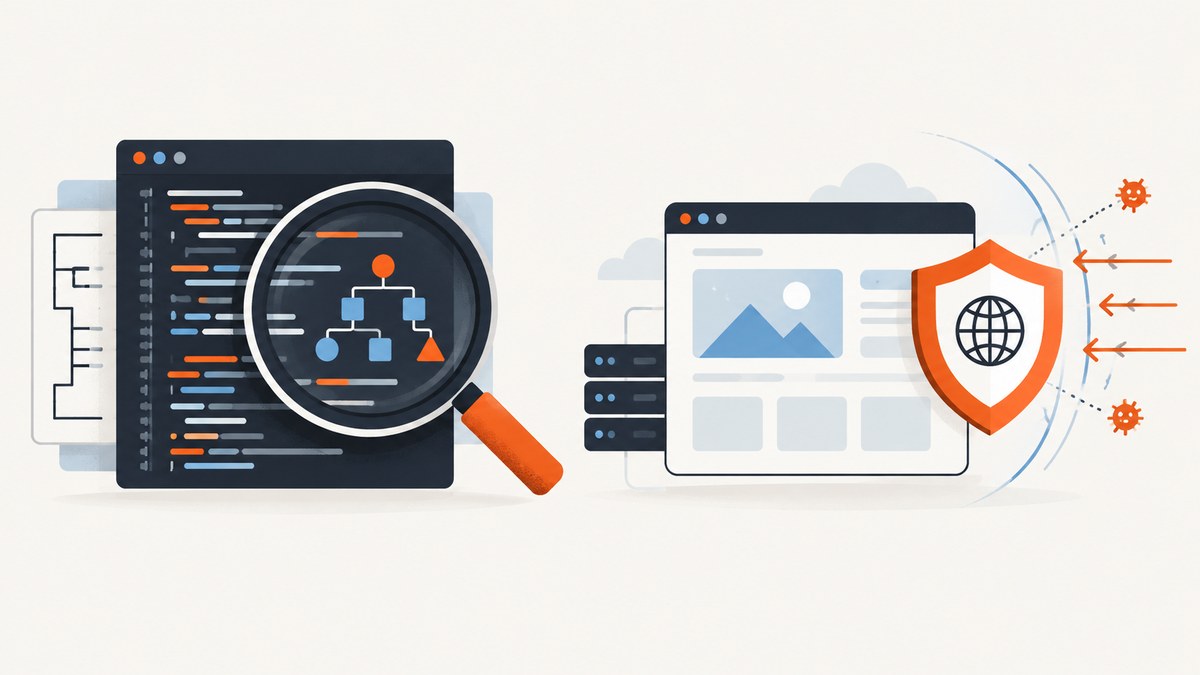
Short answer: SAST and DAST solve different parts of application security. SAST (static application security testing) analyzes source or compiled code without executing it, so it gives developers early, code-specific feedback in pull requests and builds. DAST (dynamic application security testing) probes a running application from the outside, so it can expose deployment, configuration, authentication, session, header, and component-interaction problems. For an internet-facing, regulated, or multi-service application, use both, then add threat modeling and manual testing for business logic.
NIST defines a static-code analyzer as a tool that analyzes source code without executing it (NISTIR 8011, Volume 4). OWASP describes DAST as a black-box test in which the tool has no access to source code and examines a running application from the outside (OWASP Developer Guide).
1. SAST and DAST in one view
| Question | SAST | DAST |
|---|---|---|
| What does it inspect? | Source, bytecode, or compiled artifacts | Responses and behavior of a running service |
| When does it run? | IDE, pull request, commit, or build | After deployment to staging or another authorized target |
| Typical findings | Unsafe APIs, injection paths, hard-coded secrets, tainted data flows | Injection behavior, broken authentication, access control, session issues, headers, error disclosure, integration defects |
| Remediation detail | Can point to a file, line, and data flow | Shows an endpoint, request, and response; usually cannot identify the exact source line |
| Coverage limits | May flag unreachable code and cannot see production configuration | Only reaches discovered paths and cannot inspect hidden source paths |
| Operational risk | Runs against code or build artifacts | Can change state or generate load; use isolated environments and safe accounts |
| Primary owner | Developers and code owners | Application security, platform, and service owners |
2. What SAST finds well
SAST follows syntax, control flow, and data flow without starting the application. Rules can identify a user-controlled value reaching a SQL query, an unsafe deserialization call, weak cryptography, command execution, or credentials committed to a repository. Because the result is attached to code, a developer can usually open the finding directly in an editor and propose a fix during review.
Strengths
- Fast feedback: a pull-request scan can run before merge or deployment.
- Broad repository coverage: it can inspect files and branches that a black-box crawler will never reach.
- Precise triage: data-flow traces and line locations help identify the change that introduced a defect.
- Policy enforcement: teams can fail a build for new critical findings while allowing an existing, reviewed baseline.
What SAST cannot prove
A finding is a code-level signal, not proof that an attack works in production. A flagged path may be unreachable, sanitized by a framework, or protected by a runtime control. SAST also cannot observe deployed headers, TLS settings, identity-provider configuration, network policy, feature flags, or failures that occur only when services interact. Every result needs developer triage and, for high-impact issues, a runtime check.
3. What DAST finds well
DAST sends requests to a deployed target and evaluates status codes, headers, bodies, redirects, cookies, and state changes. It can reveal reflected or stored injection, authentication and logout defects, insecure session cookies, missing security headers, verbose errors, broken access control, and integration mistakes that appear only after components are assembled.
DAST requirements
- Authorized scope: document domains, paths, methods, rate limits, and test windows.
- Representative deployment: staging should use the same routing, identity, proxy, and security configuration as production where possible.
- Test identities: provide accounts for anonymous, normal, privileged, and tenant-isolated roles.
- State and workflows: configure login, CSRF tokens, multi-step forms, file uploads, and API tokens explicitly.
- Safe data: use disposable records and prevent email, payment, or destructive actions from reaching real systems.
DAST can miss code that route discovery never reaches, including administrative paths, rarely used API operations, and workflows hidden behind client-side state. It also cannot explain the precise source line. Feed it an OpenAPI description or an authenticated route list when available, and pair results with server logs so triage can connect an observed request to code.
4. Which is better for your situation?
| Your main question | Start with | Reason |
|---|---|---|
| Can we stop unsafe patterns before merge? | SAST | It runs on every change and points to code. |
| Is the deployed service configured safely? | DAST | It tests the behavior users and attackers can reach. |
| Do sessions, roles, and tenant boundaries work? | DAST plus manual checks | Stateful, authenticated behavior is runtime-specific. |
| Do we need broad repository coverage? | SAST | It can inspect unreached files and branches. |
| Are we internet-facing, regulated, or highly distributed? | Both | Each method covers blind spots in the other. |
Use SAST first when developer speed and prevention are the priority. Use DAST first when deployment configuration, exposed endpoints, or authentication behavior is the immediate risk. In a mature program, SAST runs continuously in CI and DAST runs against every representative release candidate, with scheduled deeper scans.
5. A practical CI/CD implementation
- Define scope and policy. Name repositories, environments, test accounts, data rules, allowed request rates, and non-destructive requirements.
- Baseline SAST. Run a scan on pull requests and the default branch. Record existing findings so the first rollout does not fail every build.
- Set gates. Fail on new critical or high-confidence findings; let owners approve documented exceptions with an expiry date.
- Deploy staging. Build the same artifact intended for release, then apply production-like routing, headers, identity, and feature flags.
- Run authenticated DAST. Supply a route specification and test accounts. Start with a passive or low-impact scan, then schedule active checks in an isolated window.
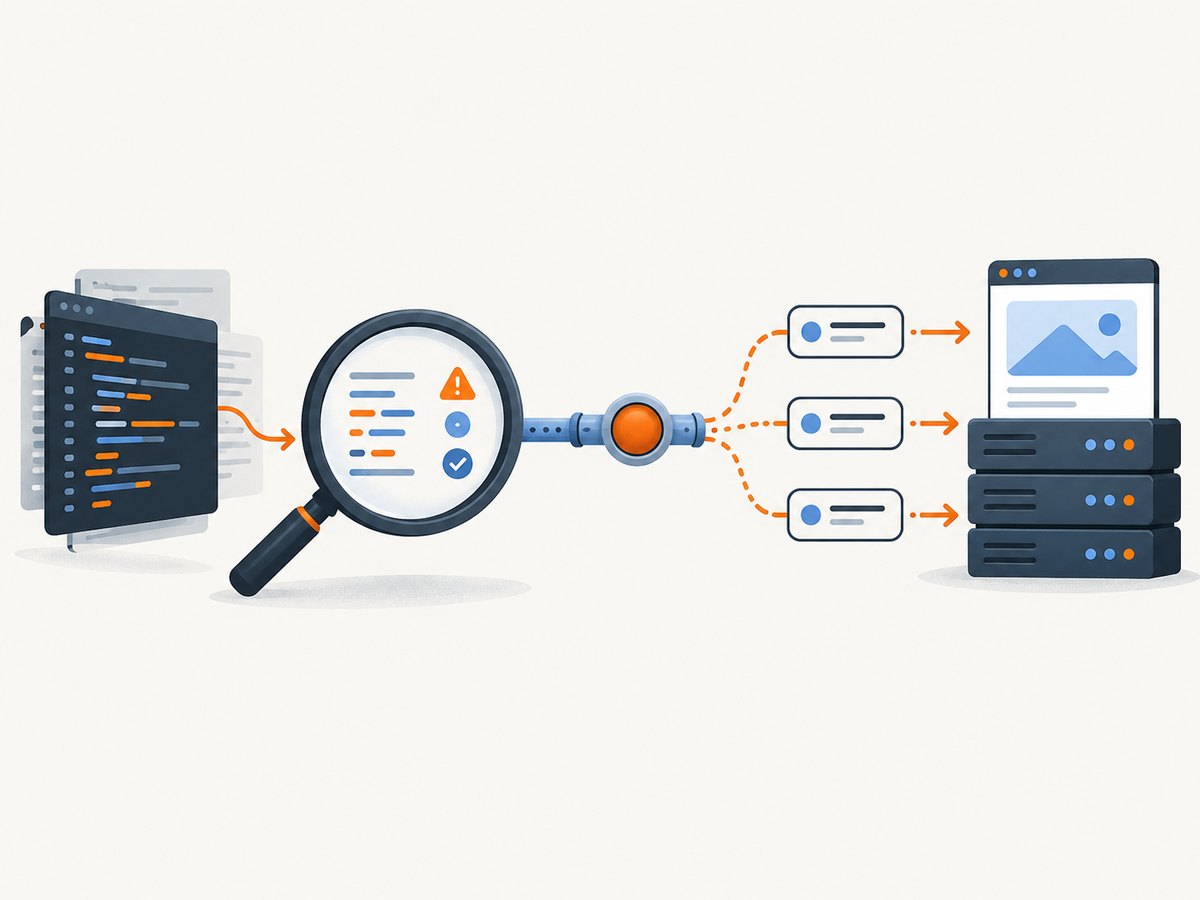
- Correlate and verify. Deduplicate SAST and DAST results, reproduce high-severity issues, fix them, and rerun both tools.
- Track outcomes. Measure open findings by severity, age, owner, and mean time to remediate rather than counting raw scanner alerts.
Example: OWASP ZAP baseline scan in a pipeline
OWASP ZAP is an open-source DAST option. Its official download page provides packages for Windows, Linux, macOS, cross-platform use, and Docker (ZAP download page). A baseline scan is a useful low-impact starting point:
docker run --rm -t \
  -v "$PWD:/zap/wrk/:rw" \
  ghcr.io/zaproxy/zaproxy:stable \
  zap-baseline.py \
  -t https://staging.example.com \
  -r zap-report.html \
  -J zap-report.json
Replace the target with an environment you own. Baseline mode does not replace an authenticated, active assessment. For APIs and multi-step applications, provide an OpenAPI definition, authentication context, and explicit exclusions according to your scanner’s current documentation.
6. Configuration details that determine coverage
SAST configuration
- Select language and framework rules that match the repository; irrelevant rules create noise.
- Enable taint or data-flow analysis for user input crossing trust boundaries.
- Exclude generated files and vendored dependencies only when they are scanned elsewhere.
- Keep a versioned baseline and review suppressions with an owner and expiration.
- Export SARIF or your CI system’s native format so findings appear beside commits.
DAST configuration
- Set crawl depth, route allowlists, and request-rate limits to protect the environment.
- Configure login scripts, bearer tokens, cookies, CSRF handling, and role-specific accounts.
- Include JSON, GraphQL, and OpenAPI routes that a browser crawler cannot discover.
- Exclude logout, delete, purchase, email, and other destructive actions unless they are safely mocked.
- Capture request and response evidence, timestamps, scanner version, and target build identifier.
7. Troubleshooting common failures
| Symptom | Likely cause | Fix |
|---|---|---|
| SAST reports hundreds of issues on the first run | No baseline or unsuitable rules | Baseline reviewed legacy findings, tune language/framework rules, and gate only new high-confidence results. |
| SAST marks safe code as vulnerable | Unreachable path, sanitizer unknown to the analyzer, or runtime control | Trace the data flow, add a documented sanitizer model or suppression, and confirm behavior with a targeted test. |
| DAST finds only the home page | Client-side routes or authentication were not supplied | Import an API specification, configure browser login, and provide a route allowlist. |
| Authenticated scan returns 401 or 403 | Expired token, missing CSRF value, wrong role, or proxy issue | Create dedicated test accounts, refresh credentials, verify headers and cookies, and inspect scanner traffic. |
| Staging becomes slow or unstable | Active checks or crawl rate are too aggressive | Lower concurrency, limit paths, scan an isolated replica, and schedule active tests off peak. |
| DAST reports a finding that cannot be reproduced | Transient state, feature flag, cache, or environment drift | Save the request and response, record the build ID, disable cache where appropriate, and rerun against the same artifact. |
| Fixes do not close findings | Duplicate alerts, stale evidence, or a different deployed build | Deduplicate by endpoint and root cause, verify the deployed commit, then rescan. |
8. Performance, reliability, and cost considerations
SAST usually adds predictable compute time to a build and can be parallelized by repository or module. Full-repository analysis may be slower than an incremental pull-request scan, so use both: fast changed-file feedback and a scheduled full scan.
DAST duration depends on route count, authentication, crawl depth, response latency, and active checks. Keep a small smoke scan on release candidates and run deeper scans on a schedule. Pin scanner versions, retain reports with the tested build identifier, and monitor the target while scans run. A scanner finding is only reliable when the target was reachable, credentials were valid, and the intended routes were exercised.
Budget for the whole workflow: CI minutes and analyzer licenses for SAST, staging capacity and test-data resets for DAST, and engineering time for triage. Do not compare tools by alert count or an unverified accuracy percentage; the research for this comparison identified no authoritative general benchmark.
9. Or skip the browser setup
When you need a visual record of a staging page, security report, or authenticated route, ScreenshotNeo can capture a URL with one GET request instead of maintaining browser automation. Cookie and consent banners, newsletter popups, and chat widgets are removed before the shot. Bot checks, blank pages, failed loads, timeouts, and cache hits are not billed, and the response identifies the result with X-Page-Verdict and X-Billed headers. Its MCP server provides take_screenshot, get_page_info, and capture_pdf tools for Claude, Cursor, and other MCP clients.
See the ScreenshotNeo documentation for all options.
curl -G "https://api.screenshotneo.com/v1/shot" -d access_key=YOUR_API_KEY --data-urlencode url=https://staging.example.com -o shot.webpimport requests
r = requests.get("https://api.screenshotneo.com/v1/shot", params={"access_key": "YOUR_API_KEY", "url": "https://staging.example.com"}, timeout=90)
open("shot.webp", "wb").write(r.content)const q = new URLSearchParams({ access_key: 'YOUR_API_KEY', url: 'https://staging.example.com' });
const res = await fetch(`https://api.screenshotneo.com/v1/shot?${q}`);ScreenshotNeo includes full-page and element captures, custom headers and cookies for authorized staging pages, waits for selectors or network idle, custom CSS and JavaScript, PDF output, caching, signed links, asynchronous jobs, bulk capture, and usage reporting. The Free plan includes 1,000 screenshots each month with no card; paid plans start at $5 for 3,000. Create a free ScreenshotNeo account.
10. What neither SAST nor DAST replaces
Automated tools lack complete application-specific context. They cannot reliably judge business-logic abuse such as fraud workflows, harmful authorization combinations, or a valid action performed in the wrong sequence. Add threat modeling for design decisions, manual penetration testing for attack chains, and focused tests for authorization and business rules. OWASP’s Web Security Testing Guide is a useful planning reference.
11. FAQ
Can SAST find runtime vulnerabilities?
It can identify code patterns that may cause a runtime vulnerability, but it cannot verify deployed configuration, reachable routes, headers, or service interaction. Use DAST or a targeted runtime test to confirm those conditions.
When should I run DAST?
Run a low-impact scan against each representative release candidate and schedule deeper authenticated scans against an isolated staging environment. Repeat after major routing, identity, or infrastructure changes.
Do small teams need both?
Start with the method that matches your largest current risk, then add the other as soon as the basic workflow is stable. Even a small internet-facing service benefits from early SAST plus periodic DAST.
Why do SAST and DAST disagree?
They observe different layers. SAST may flag a theoretical or unreachable path; DAST may observe a runtime control or miss the path entirely. Correlate evidence and review the application context instead of treating either result as absolute.
Is a clean DAST report proof that the application is secure?
No. It proves only that the configured scanner did not identify issues in the routes and states it reached. Threat modeling, manual testing, and business-logic review remain necessary.
12. Implementation checklist
- Authorize domains, paths, accounts, data, and scan windows.
- Run SAST on pull requests and main-branch builds with a reviewed baseline.
- Deploy a production-like staging artifact for DAST.
- Provide authenticated workflows, API specifications, and safe exclusions.
- Gate new high-confidence findings and assign every exception an owner.
- Save evidence with scanner version and build identifier.
- Correlate findings, verify fixes, and track remediation time.
- Schedule threat modeling and manual testing for business logic and attack chains.