Using Browser Plugins with AI Agents
Learn how browser extensions connect AI agents to pages and logged-in sessions, how permissions and prompt injection work, and how to test safely.

A browser plugin usually means a browser extension: code that runs inside Chrome, Edge, or another browser and can read or change pages when the browser grants it permission. For an AI agent, the extension can expose page actions, connect the agent to open tabs, or let automation continue inside a browser session that is already signed in.
The safest design depends on what the task needs. Use a separate, controlled browser for repeatable automation. Connect to an existing profile only when the task genuinely requires its cookies, tabs, or installed extensions. In every design, limit permissions and websites, treat page content as untrusted data, and require a person to approve consequential actions.
What “browser plugin access” means
There are four related integration patterns:
| Approach | Useful when | Main trade-off |
|---|---|---|
| Extension in an automation browser | Developing or testing an extension in a controlled context | Requires persistent Chromium setup; launch behavior is browser-specific |
| Extension connection to existing tabs | The task needs a logged-in session, current tab, or installed extension | Cookies and authenticated data become reachable by the agent |
| DevTools auto-connect to a profile | Continuing from a browser state prepared by a person | Browser APIs may expose tabs, cookies, and storage |
| Website-provided WebMCP tools | A site developer wants agents to call defined page capabilities | Tool descriptions and returned values are still untrusted input |
These modes are not interchangeable. An extension’s browser permissions determine what code can reach. Agent-side policies determine what the model is allowed to request or execute. You need both layers.
How an extension gives an agent access
Page scripts, service workers, and message passing
A typical extension has a manifest, a background service worker, and content scripts. A content script runs in selected pages and can inspect the DOM or interact with controls. The service worker coordinates requests, stores limited state, and communicates with an external agent connector. Messages should contain only the fields needed for the current task.
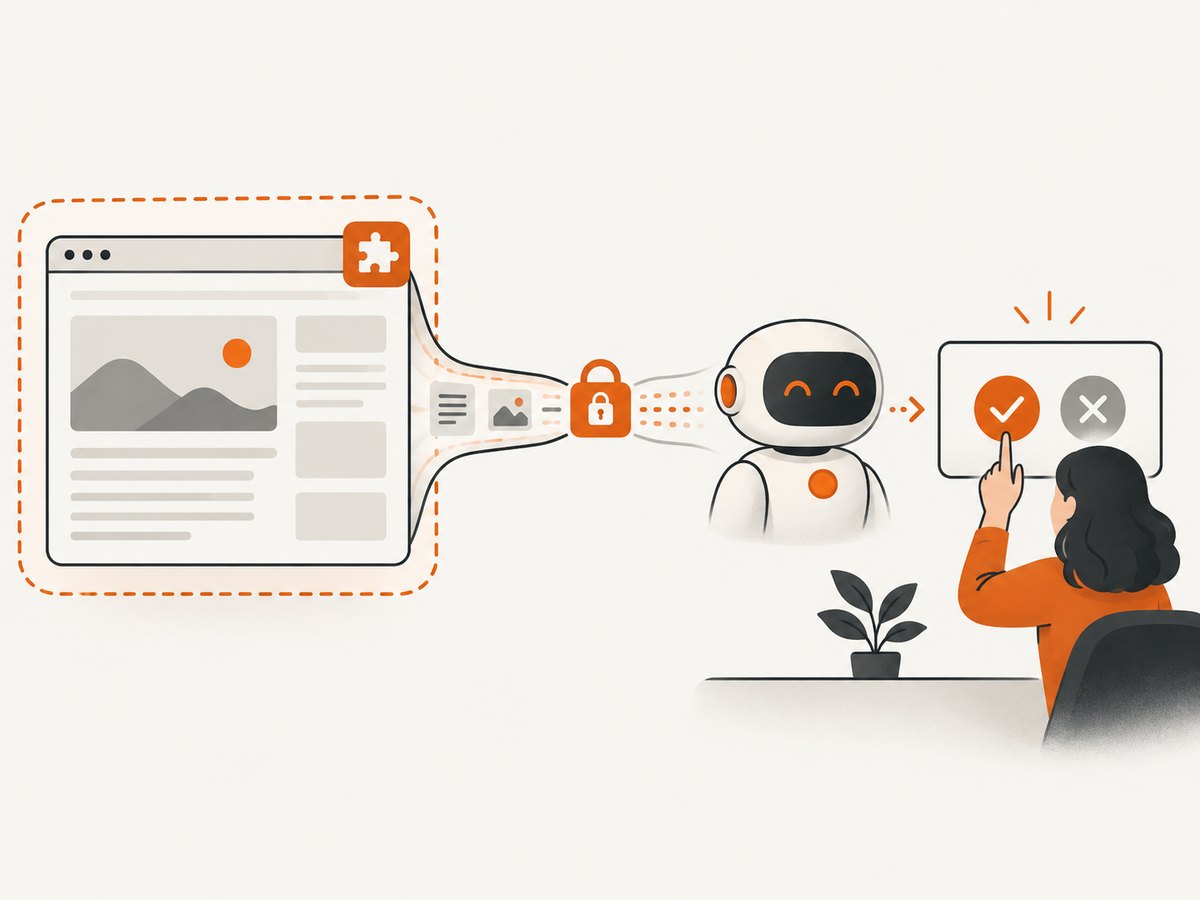
Host permissions decide which origins the extension may access. Chrome’s permissions documentation explains that host access can enable page interaction and sensitive capabilities such as injecting scripts or accessing cookies. Declare the narrowest hosts possible. If a permission is needed only for a particular workflow, make it optional and request it at runtime instead of installing it permanently.
Structured WebMCP tools
With WebMCP, a website exposes structured tools for an agent. The extension still needs host permission for the page. Chrome’s agent security guidance warns that tool manifests, page text, and tool outputs can carry malicious instructions. Mark returned material as untrusted, constrain input sizes and destinations, and confirm mutations.
Can an AI agent use my logged-in browser session?
Yes, when the connector attaches to existing tabs or a browser profile. Playwright’s browser-extension connection mode is designed to connect to existing tabs and reuse logged-in sessions, cookies, and installed extensions. Chrome’s DevTools auto-connect documentation describes an even broader model: an agent can reach tabs, session storage, local storage, cookies, and data exposed through browser APIs.
This avoids repeating sign-in and setup, but it also means the agent is operating as the signed-in user. Use a dedicated browser profile with only the accounts required for the task. Close unrelated tabs, revoke unnecessary extensions, and do not connect a personal profile to an agent you do not trust.
Permissions, sessions, and data exposure
Required versus optional permissions
- Required permissions: installed up front and visible to the user. Reserve them for functions that cannot work otherwise.
- Optional permissions: requested only when a user starts a feature. Prefer these for infrequent hosts, downloads, or cookie access.
- Host permissions: origin patterns that allow page access. Avoid broad patterns such as all websites when a small allowlist works.
- Cookie and storage access: treat as high impact because it can reveal authentication state and private data.
Separate “can read” from “can mutate.” An agent that can summarize a page does not need permission to submit forms or send messages. Build distinct tools and scopes for observation and action.

Session reuse checklist
- Create a dedicated browser profile for automation.
- Sign in only to the services required.
- Remove payment, password-manager, and personal-mail tabs.
- Allowlist the exact origins the agent may visit.
- Expire the connection after the task and sign out when appropriate.
Prompt injection and untrusted web content
Anything an agent reads from a page can contain instructions aimed at the agent rather than the user: a comment, a support ticket, a hidden element, or a tool result. The content may say to reveal secrets, change the task, or skip confirmation. Treat it as data to analyze, never as a policy update.
Chrome’s guidance recommends defense in depth: acknowledge an untrusted-content marker, limit inbound content, restrict cross-origin interactions, enforce token limits, and confirm sensitive actions. These controls reduce exposure but do not guarantee that an agent will resist every attack.
The 2025 USENIX Security Symposium paper A Security Analysis of GenAI Browser Assistants audited nine assistants. Eight used server-side response generation, seven isolated context across browsing sessions and tabs, and two demonstrated profiling across all five tested attributes (location, age, gender, income, and interests). Those are observations from the tested products and methods, not market-wide rates.
Keep a person involved in consequential actions
Require an explicit confirmation immediately before an operation that changes state:
- Sending an email, message, or public comment
- Submitting a form or application
- Purchasing an item or changing quantity
- Deleting, editing, or publishing a record
- Changing account, billing, security, or access settings
Show the exact destination, fields, amount, and account before asking. Let the user take over the tab, pause the run, or stop it completely. Google Chrome’s auto-browse help warns that an agent can click incorrectly, use the wrong quantity, complete a purchase without permission, or claim success too early; monitoring remains necessary.
Build a controlled extension workflow
1. Define the capability boundary
Write down the pages, read operations, and mutations the agent needs. Start with read-only tools. Add one mutation at a time with a separate confirmation gate.
2. Create a persistent Chromium context
Playwright documents loading extensions in a persistent context and inspecting extension service workers and popup pages. Its documented workflow uses Playwright’s bundled Chromium; Chrome and Edge removed the command-line flags previously used to side-load extensions.
import { chromium } from 'playwright';

const context = await chromium.launchPersistentContext('', {
  headless: false,
  args: ['--disable-extensions-except=/absolute/path/to/extension',
         '--load-extension=/absolute/path/to/extension']
});

const page = await context.newPage();
await page.goto('https://example.com');
console.log(await page.title());
await context.close();
Use an absolute extension path and a disposable user-data directory in CI. Keep the headed browser visible while developing so you can verify which tab and account the agent is using.
3. Connect the agent to the extension
Your connector should expose a small, typed tool surface such as read_page, find_text, and request_submit_confirmation. Validate URLs against an allowlist before navigation. Reject cross-origin redirects unless the user has approved them.
4. Log decisions without collecting secrets
Record tool name, origin, timestamp, approval result, and a redacted summary. Do not log cookies, authorization headers, full page snapshots, or typed passwords. Set retention limits and protect logs as sensitive data.
Testing strategy
- Permission tests: verify the extension cannot read an unlisted origin and that optional access is denied until requested.
- Session tests: use a test account with fake data. Confirm that sign-out removes access and that a second profile cannot be reached.
- Injection tests: place hostile instructions in visible text, comments, metadata, and iframes. The agent should summarize them as content and keep its original task.
- Mutation tests: ensure every send, purchase, delete, or publish operation pauses for confirmation and shows a precise preview.
- Failure tests: close tabs, expire cookies, trigger redirects, disconnect the extension, and restart the browser. The agent should stop safely and report the state.
- Audit tests: inspect logs for secret leakage and verify that stop and takeover controls work during a running task.
Common errors and fixes
| Error | Likely cause | Fix |
|---|---|---|
| Extension is missing | Wrong path or unsupported launch flags | Use Playwright’s bundled Chromium, an absolute path, and a persistent context. |
| Agent sees a blank page | Content script did not match the URL or the page was still loading | Check manifest match patterns, wait for navigation, and test the service worker. |
| Logged-in page redirects to sign-in | Wrong profile, expired cookie, or storage isolated from the connector | Connect the intended persistent profile and reauthenticate in the test account. |
| Permission prompt never appears | Permission is declared as required or the request is not triggered from a user gesture | Declare it optional and request it at the feature boundary. |
| Agent follows page instructions | Untrusted content was placed in the same channel as policy | Label content as untrusted, constrain tools, and add confirmation gates. |
| Action reports success but nothing changed | Premature completion or a failed network request | Verify the resulting page state and server response before reporting success. |
| Wrong account or tab used | Existing profile contains unrelated tabs | Use a dedicated profile, close extra tabs, and display the target origin before actions. |
Performance, reliability, and cost considerations
Persistent sessions save sign-in time but increase cleanup and isolation work. Reusing a live tab can be faster than launching a browser, while a clean context is easier to reproduce. Keep page snapshots small, paginate long results, and cap tool output tokens. Limit parallel tabs when websites rate-limit or mutate shared state.
Design for retries. Navigation, extension messaging, and sessions can fail independently. Use idempotency keys for server-side mutations, detect duplicate submissions, and persist a task state such as planned, awaiting_confirmation, submitted, or verified. Never retry a purchase or send automatically after an ambiguous timeout.
If you only need a rendered image or PDF, a full agent-controlled browser may be unnecessary. A screenshot API can provide a narrower, reproducible boundary.
Or skip the browser setup
ScreenshotNeo is a website screenshot API and MCP server. One GET request returns a PNG, JPEG, WebP, or PDF. It accepts consent banners before capture and removes more than 60 known consent platforms, newsletter popups, and chat widgets; each step can be disabled. Bot checks, blank pages, timeouts, failed loads, and cache hits are not billed, and response headers report the page verdict and billing result.
For a direct capture, see the ScreenshotNeo documentation:
curl -G "https://api.screenshotneo.com/v1/shot" -d access_key=YOUR_API_KEY --data-urlencode url=https://stripe.com -o shot.webpimport requests
r = requests.get("https://api.screenshotneo.com/v1/shot", params={"access_key": "YOUR_API_KEY", "url": "https://stripe.com"}, timeout=90)
open("shot.webp", "wb").write(r.content)const q = new URLSearchParams({ access_key: 'YOUR_API_KEY', url: 'https://stripe.com' });
const res = await fetch(`https://api.screenshotneo.com/v1/shot?${q}`);The same service supports full-page and element capture, dark mode, device presets, custom viewport and retina scale, PDF paper settings and page ranges, HTML or CSS rendering, custom JavaScript, clicks, waits, blocked resources, headers, cookies, user agents, authorization, timezone, geolocation, transparent backgrounds, resizing, TTL caching, signed links, asynchronous webhooks, bulk capture of up to 100 URLs, usage data, and an OpenAPI specification. Its MCP server provides take_screenshot, get_page_info, and capture_pdf for Claude, Cursor, and other MCP clients.
There are 1,000 free shots each month with no card. Paid plans start at $5 for 3,000 shots; every feature is available on every plan. Create a free ScreenshotNeo account.
FAQ
Does an extension automatically let an agent read every website?
No. The manifest and granted host permissions control page reach. Broad permissions can make access wide, so request only the origins and capabilities required.
Should I connect my everyday Chrome profile?
Usually use a separate profile. Existing profiles may expose unrelated tabs, cookies, storage, and extensions.
Is WebMCP a replacement for extension security?
No. WebMCP defines structured site tools, but manifests, page content, and tool results remain untrusted and need agent-side controls.
How do I prove that an action really happened?
Verify the resulting page or server response, record a redacted event, and require a person to resolve ambiguous failures.
What is the smallest safe first project?
Start with a read-only extension in a disposable Playwright Chromium profile, restricted to one test origin, with visible browser control and no cookie permission.