How to Create Universal Website Embeds
Build reusable website embeds with responsive iframes, oEmbed providers, security controls, troubleshooting, and a hosted screenshot alternative.
Short answer: create a reusable embed component that accepts only approved provider URLs, renders a responsive <iframe> when the source permits framing, and uses oEmbed when a provider publishes embed metadata. There is no single method that can embed every URL. The source site can deny framing with Content Security Policy, the consumer can restrict frame sources, and browser privacy controls can affect cookies and login state.
This guide shows how to build a practical “universal” embed system, make iframes responsive, support oEmbed providers safely, handle WordPress, diagnose blocked frames, and choose between direct iframe markup and a provider integration. It also includes a hosted screenshot option when you need a visual representation instead of a live interactive frame.
1. What “universal embed” really means
A universal embed should mean one reusable integration pattern, not a promise that any URL can be displayed inside any other site. A browser will load a frame only when the framed site allows the parent origin and the parent page’s own policy allows the source. Authentication, third-party cookies, sandbox permissions, and provider-specific rules add more limits.
There are two practical models:
- Direct iframe: you already know the provider and its documented embed URL. This is the simplest option for a video, dashboard, form, map, or hosted report.
- oEmbed consumer: your application accepts a supported resource URL, resolves it through the provider’s oEmbed endpoint, validates the response, and renders a consistent component. oEmbed describes “a format for allowing an embedded representation of a URL on third party sites” (oEmbed specification).
Neither method overrides a provider’s refusal to be framed. If a publisher sends a restrictive Content-Security-Policy: frame-ancestors header or a legacy framing header, the browser blocks the page before your JavaScript can repair it.
2. Start with a responsive iframe
For a known source, use the provider’s documented embed URL rather than guessing a normal page URL. Give the frame a descriptive title, defer off-screen loading when appropriate, and add only the permissions required by the feature.
<div class="embed-frame">
  <iframe
    src="https://provider.example/embed/resource-id"
    title="Description of the embedded resource"
    loading="lazy"
    allowfullscreen>
  </iframe>
</div>
.embed-frame {
width: 100%;
aspect-ratio: 16 / 9;
}
.embed-frame iframe {
display: block;
width: 100%;
height: 100%;
border: 0;
}An aspect ratio works well for video and visual media. Forms, dashboards, documents, and long pages often need a deliberate minimum or fixed height instead:
.embed-frame--form {
  min-height: 640px;
  aspect-ratio: auto;
}

@media (max-width: 600px) {
  .embed-frame--form {
    min-height: 760px;
  }
}
loading="lazy" lets the browser delay loading until the frame is near the viewport. Do not lazy-load a frame that must be immediately available for the first interaction or that is the primary content above the fold.
Use sandbox deliberately
Sandboxing reduces what an untrusted frame can do, but it can also break forms, popups, downloads, scripts, or PDF viewers. Begin with the smallest permission set and test the actual provider.
<iframe
  src="https://provider.example/embed/resource-id"
  title="Embedded report"
  sandbox="allow-scripts allow-forms"
  referrerpolicy="strict-origin-when-cross-origin">
</iframe>
Be especially careful with allow-scripts and allow-same-origin on a same-origin frame. MDN warns that this combination can let the embedded document remove its sandbox. Read the iframe reference before adding permissions.
3. Make content sizing reliable
The parent page cannot normally inspect the rendered height of a cross-origin iframe. This is a browser security and privacy boundary, so a generic “read the iframe height” script is not a reliable universal solution.
Use one of these approaches:
- Choose an aspect ratio or a known height for the component.
- Ask the provider whether it exposes a resize protocol.
- If you control both origins, use
window.postMessagewith strict origin checks. - Use a provider capability such as
responsive-embedded-sizingand itsWindow.requestResize()mechanism when supported by the target browser and embedded document.
When using postMessage, never accept a message from * without validation:
const allowedOrigin = "https://provider.example";

window.addEventListener("message", (event) => {
  if (event.origin !== allowedOrigin) return;
  if (!event.data || event.data.type !== "embed-resize") return;

  const height = Number(event.data.height);
  if (!Number.isFinite(height) || height < 120 || height > 5000) return;

  const frame = document.querySelector("iframe[data-embed]");
  if (frame) frame.style.height = `${Math.round(height)}px`;
});
The embedded side must send the message, and it must use the exact parent origin. If the provider does not cooperate, use a stable layout rather than attempting to bypass the browser boundary.
4. Allow framing with CSP
If you control the framed site, set frame-ancestors in its HTTP response. This policy belongs to the embedded site; adding an iframe on the consumer page cannot override a denial.
Content-Security-Policy: frame-ancestors 'self' https://www.example.comList only the parent origins that should embed the page. Avoid a broad wildcard when the set is known. The MDN frame-ancestors documentation explains how the directive is evaluated.
The consumer has a separate responsibility: its own CSP must permit the frame source. For example:
Content-Security-Policy: default-src 'self'; frame-src https://provider.exampleDeploy a new consumer policy in report-only mode first when possible, inspect violations, and then enforce it. Do not confuse frame-ancestors (who may embed your page) with frame-src (which frames your page may load).
5. Build an oEmbed consumer for supported providers
oEmbed works when a provider publishes an endpoint or discovery metadata for a resource URL. It supports resource types such as photo, video, link, and rich content. Provider coverage is explicit; an arbitrary website does not become embeddable merely because your application accepts its URL.
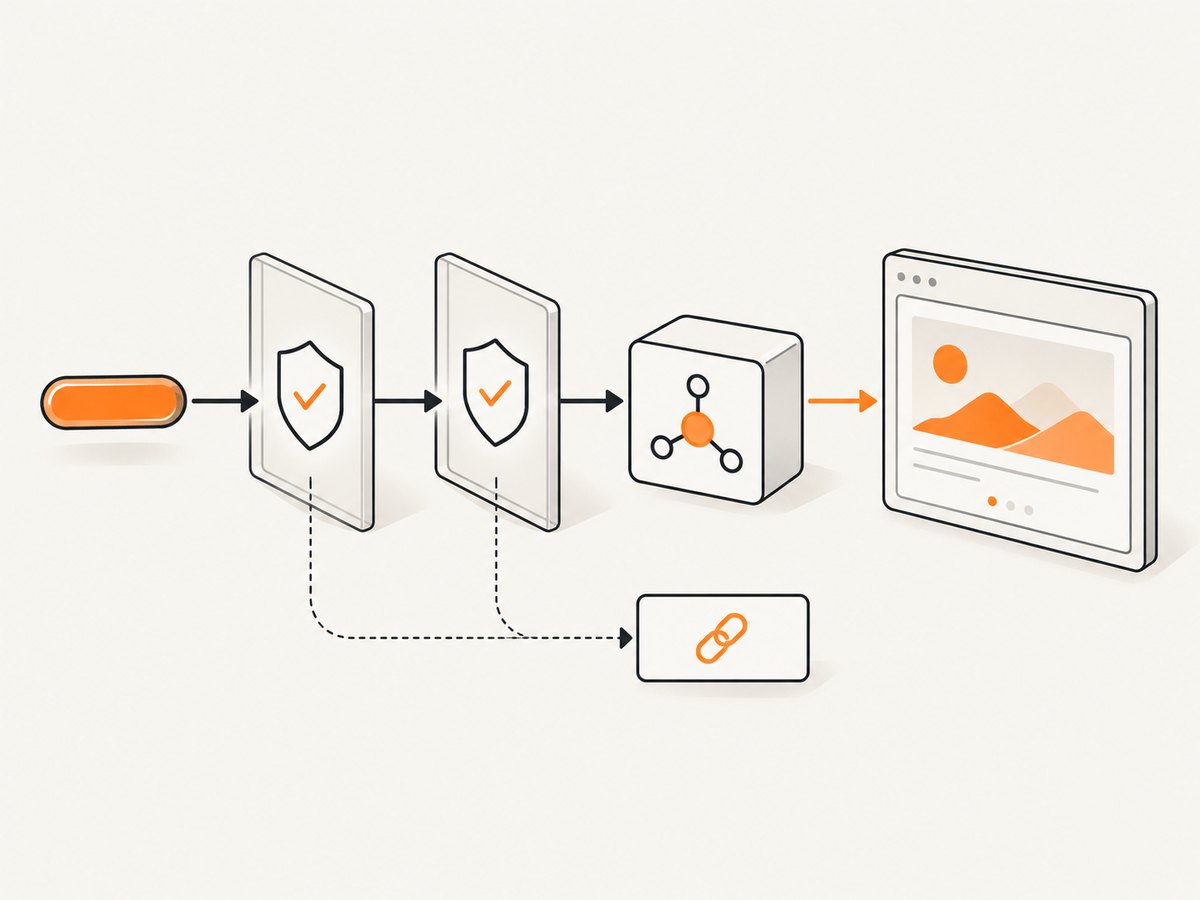
A safe resolution pipeline
- Accept a URL from a trusted editor or user input field.
- Parse it and match it against a small allowlist of provider hostnames and URL patterns.
- Resolve only approved patterns through configured oEmbed endpoints or a maintained library.
- Validate the response type, URL, dimensions, title, author fields, and maximum HTML size.
- Escape text fields. Filter returned HTML through a strict element and attribute allowlist.
- Render the result in an accessible responsive component, with a normal link fallback.
Do not create a server endpoint that fetches any URL supplied by a user. That architecture can become an unsafe proxy and may expose internal network resources. Validate redirects, restrict destination hosts, apply timeouts, cap response size, and log provider failures without storing sensitive content.
Example provider configuration
const providers = [
  {
    name: "Example Video",
    hosts: new Set(["video.example"]),
    matches: (url) => url.pathname.startsWith("/watch/"),
    endpoint: "https://video.example/oembed"
  }
];

function findProvider(input) {
  const url = new URL(input);
  return providers.find((provider) =>
    provider.hosts.has(url.hostname) && provider.matches(url)
  );
}

async function resolveOembed(input) {
  const provider = findProvider(input);
  if (!provider) throw new Error("Unsupported provider URL");

  const endpoint = new URL(provider.endpoint);
  endpoint.searchParams.set("url", input);
  endpoint.searchParams.set("format", "json");

  const response = await fetch(endpoint, {
    signal: AbortSignal.timeout(5000)
  });
  if (!response.ok) throw new Error(`Provider returned ${response.status}`);

  const data = await response.json();
  if (!["photo", "video", "link", "rich"].includes(data.type)) {
    throw new Error("Unsupported oEmbed type");
  }
  if (typeof data.html === "string" && data.html.length > 200000) {
    throw new Error("oEmbed HTML is too large");
  }
  return data;
}
When the response contains provider HTML, sanitize it before inserting it into the document. A safer alternative is to ignore returned HTML and build your own iframe from validated provider fields. WordPress follows this general principle: it supports a maintained provider whitelist and filters discovered output.
6. WordPress and other CMS platforms
WordPress uses oEmbed for supported URLs, but its core whitelist does not include every provider. Administrators can register providers or custom handlers. WordPress documentation describes filtering discovered HTML and applying additional restrictions, so bypassing those protections should be limited to trusted privileged users. See the WordPress oEmbed documentation.
For any CMS, document the supported provider list, show editors the normal-link fallback, and keep provider configuration in code or an administrator-only setting. A “paste any URL” field should not silently fetch arbitrary destinations.
7. Why won’t this website load in an iframe?
Use the browser console and Network panel, then work through this checklist:
| Symptom | Likely cause | Fix |
|---|---|---|
| “Refused to frame” or CSP error | The source sends restrictive frame-ancestors. |
Ask the owner for an official embed URL or permission. You cannot override it from the parent page. |
| Blank frame with no obvious error | Wrong URL, redirect to a non-embeddable page, or provider script failure. | Open the final URL directly, inspect redirects and response headers, and use the provider’s documented embed route. |
Browser reports X-Frame-Options |
A legacy framing header denies the parent. | Change the source configuration or use an official API, link, or screenshot. |
| Frame loads but sign-in fails | Third-party cookie or SameSite restrictions. | Use a provider-supported authentication flow, custom domain, or top-level navigation. Do not weaken cookie security blindly. |
| Form or popup stopped working | The sandbox lacks a required capability. | Add only the specific permission required, such as allow-forms or allow-popups, and retest. |
| Content is clipped | Fixed height or unsupported resize protocol. | Use an appropriate minimum height, provider resize API, or a separate page view. |
| Consumer CSP blocks the frame | frame-src does not include the provider. |
Update the consumer policy and verify the exact scheme and hostname. |
| oEmbed returns 404 | The provider does not support that resource pattern or endpoint. | Remove it from the supported list or use the provider’s documented integration. |
| oEmbed HTML creates a security review issue | Unfiltered provider markup is being injected. | Sanitize it, render a controlled iframe, or isolate it on a separate origin. |
8. Performance, reliability, and cost
Live frames add another document, network connection, JavaScript runtime, and possible analytics workload to your page. Measure the real provider: use lazy loading for below-the-fold embeds, avoid loading multiple hidden frames, reserve layout space with aspect-ratio or min-height, and show a link fallback if a provider is slow.
For oEmbed, cache validated metadata for a short period and set strict connection and response timeouts. Cache keys should include the canonical resource URL and provider version. Treat provider outages as a normal failure mode: preserve the original link and let editors retry resolution.
Direct iframe and oEmbed generally have no separate charge from the provider unless that provider’s plan says otherwise, but they can increase your page bandwidth and client-side work. If you need a static image for previews, reports, social cards, or an archive, a screenshot avoids live-frame restrictions and is easier to cache. Confirm that your use complies with the source site’s terms and permissions.
9. Or skip the browser setup
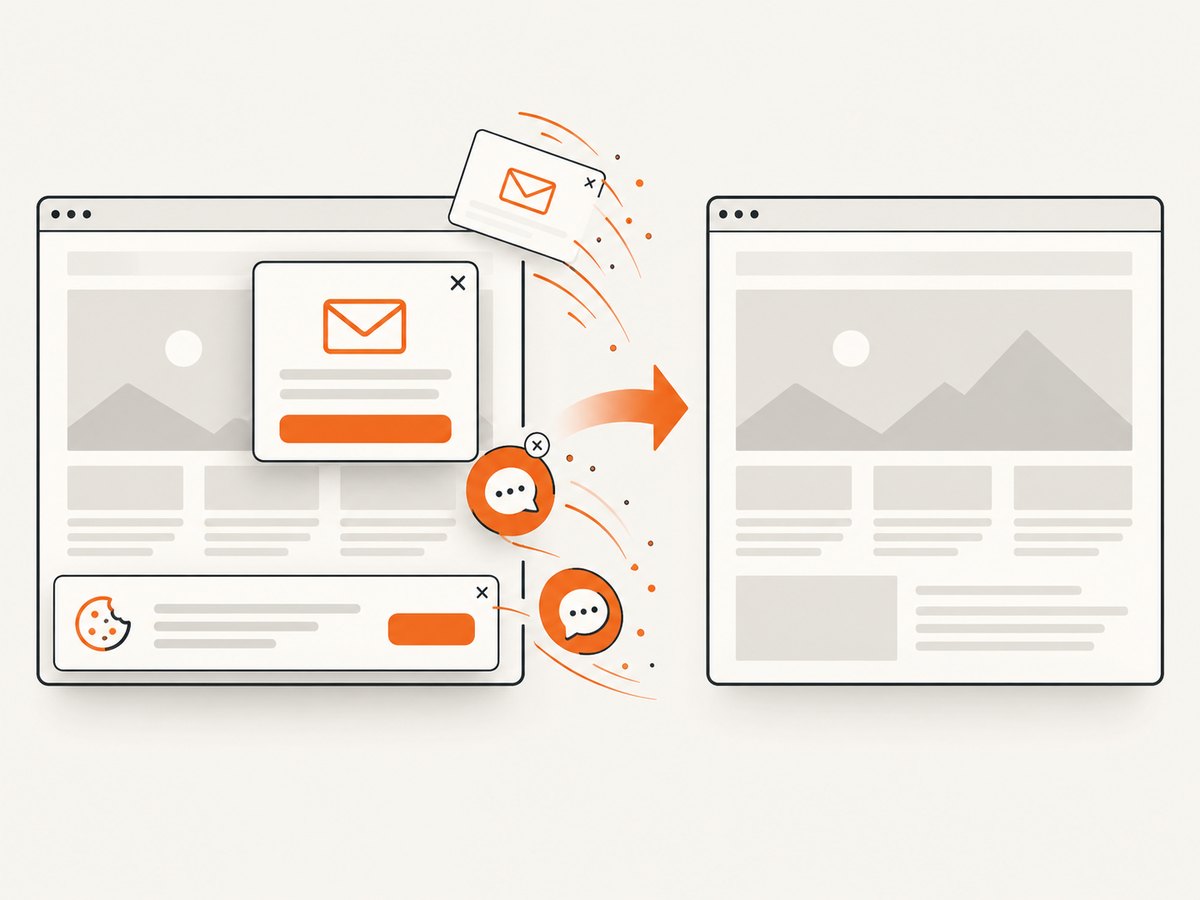
When the requirement is a visual capture rather than an interactive embed, ScreenshotNeo provides a website screenshot API and MCP server. It accepts one GET request and returns PNG, JPEG, WebP, or PDF. Before capture, it accepts cookie and consent banners and removes more than 60 known consent platforms, newsletter popups, and chat widgets; each step can be disabled. Bot checks, CAPTCHAs, blank pages, timeouts, failed loads, and cache hits are not billed, and the response identifies the result with X-Page-Verdict and X-Billed headers.
See the ScreenshotNeo API documentation for all options.
curl -G "https://api.screenshotneo.com/v1/shot" -d access_key=YOUR_API_KEY --data-urlencode url=https://stripe.com -o shot.webpimport requests
r = requests.get(
"https://api.screenshotneo.com/v1/shot",
params={"access_key": "YOUR_API_KEY", "url": "https://stripe.com"},
timeout=90,
)
open("shot.webp", "wb").write(r.content)const q = new URLSearchParams({ access_key: 'YOUR_API_KEY', url: 'https://stripe.com' });
const res = await fetch(`https://api.screenshotneo.com/v1/shot?${q}`);
const image = Buffer.from(await res.arrayBuffer());
require('fs').writeFileSync('shot.webp', image);ScreenshotNeo includes full-page capture with lazy images loaded, element capture by CSS selector, dark mode, device presets, custom viewports, retina scale, PDF paper sizes and page ranges, custom CSS and JavaScript, clicks, selector or network-idle waits, ad and tracker blocking, custom headers and cookies, timezone and geolocation, transparent backgrounds, resizing, selectable cache TTLs, signed image links, asynchronous jobs with signed webhooks, bulk capture for up to 100 URLs per call, a usage API, and an OpenAPI specification. Its parameter names are compatible with those used by other screenshot APIs, which helps when switching.
An MCP server provides take_screenshot, get_page_info, and capture_pdf tools for Claude, Cursor, and other MCP clients. The Free plan includes 1,000 shots per month with no card; paid plans start at $5 for 3,000 shots, and every feature is available on every plan. Create a free ScreenshotNeo account.
10. Security and accessibility checklist
- Allow only known provider URL patterns.
- Use HTTPS for every source and endpoint.
- Validate redirects and destination hosts server-side.
- Filter oEmbed HTML or isolate it on a separate origin.
- Use a restrictive sandbox and add capabilities one at a time.
- Set a concise, descriptive iframe
title. - Keep a normal link fallback for keyboard users, blocked frames, and outages.
- Set
frame-ancestorson pages you own. - Use the consumer’s
frame-srcpolicy to limit what your page loads. - Test forms, sign-in, downloads, popups, resizing, mobile layouts, and cookie behavior.
11. Frequently asked questions
Can I embed any website with an iframe?
No. The source can deny framing with CSP or legacy headers, and its login and cookie policies may prevent useful operation.
Is oEmbed a replacement for iframes?
No. oEmbed is a discovery and response format for supported providers. The returned representation may still be an iframe or another controlled embed.
Should I use a fixed iframe height?
Use a fixed or minimum height for forms and dashboards when their size is known. Use an aspect ratio for media. Content-aware cross-origin sizing requires provider cooperation.
How do I support a new provider?
Add its hostname and URL patterns to an explicit allowlist, configure its documented oEmbed endpoint or embed URL, validate responses, and test policy, cookies, accessibility, and failure behavior.
When is a screenshot better than a live embed?
Use a screenshot for previews, archives, reports, and static cards where interaction is unnecessary or framing is blocked. Use a live iframe when users must interact with the source.


