How to Embed a Web-Based Template Editor
Learn how to add template editing to your web app, choose the right integration model, connect templates to secure storage, and handle browser and content security.
To embed a web-based template editor, first decide what “embed” means for your product: mount an editor SDK inside your own application, build an app that runs inside another editor platform, or display a finished design on a web page. These are different integrations with different control boundaries.
If your users need to create or edit templates inside your product, choose an embeddable SDK or build an editor, then connect its project data to your own persistence and authorization layers. GrapesJS Studio SDK is one documented embeddable option; its documentation covers getting started and template configuration. Check its current license, runtime support, export format, and commercial terms before committing. GrapesJS Studio SDK documentation
This guide focuses on that first pattern, then explains the platform-hosted and published-design alternatives, implementation steps, browser constraints, security, operations, and troubleshooting.
1. Choose the kind of embed you need
| Pattern | Use it when | Who controls identity and data? |
|---|---|---|
| Editor SDK in your app | Your users edit templates as part of your product. | Your app controls accounts, persistence, and surrounding UX. The SDK constrains editor behavior and available extension points. |
| App hosted inside an editor | You are adding a capability for users of an existing editor platform. | The host controls the iframe, permissions, and exposed APIs. Your app should use documented platform APIs. |
| Published design embed | You want to display a finished design on your website. | The publisher serves the design. This is a display embed, not an editable editor SDK. |
| Rich-media embed in a design | A design needs to show supported external media. | The source and host platform control the media iframe. The supported route may accept only supported URLs, not arbitrary HTML. |
Canva documents apps running inside an iframe and interacting through the APIs the platform exposes. That does not mean the Canva editor itself can be embedded as an unrestricted interactive editor in any third-party app. If your goal is to show a published Canva design, use its published-design embed workflow and check the current sharing and access settings. Canva app documentation · Canva design embed guidance
2. Define the editing experience before choosing an SDK
Write down the editing tasks users need to complete and the outputs your product must support. That list drives the editor choice, template model, and storage design.
- What can users change: text, images, layout, colors, or arbitrary markup?
- Do they start from supplied templates, duplicate an existing project, or create a blank canvas?
- What must the product export: HTML, an image, PDF, or structured project data?
- Is the editor part of the product page, a dedicated route, or a separate window?
- Which browsers, screen sizes, keyboard workflows, and assistive technologies must work?
- Can users add scripts, embeds, external assets, or custom styles?
An SDK can provide an existing visual editing UI and extension points. A custom editor gives your team control over the experience, but your team owns the editing model, its persistence, and ongoing maintenance. Compare candidates using this checklist:
- Template and project data model, including loading, saving, duplication, and versioning.
- Supported runtime and framework integration.
- Export formats and whether data remains portable if you change editors.
- Authentication and authorization model, including server-side operations.
- UI customization, localization, accessibility, and mobile behavior.
- Allowed scripts, assets, embeds, and other browser resources.
- License, commercial terms, and operating cost for your intended use.
3. Mount an editor SDK in your application
The exact initialization code and package setup depend on the editor and its current SDK release, so use that vendor’s documentation for the SDK-specific mount call. GrapesJS Studio SDK documents an embeddable drag-and-drop visual editor and template configuration. The example below shows the host application boundary you should implement around an SDK mount; mountEditor is intentionally a placeholder for the vendor’s documented initialization API.
// Host application example: replace mountEditor with the SDK's documented API.
const root = document.querySelector('#template-editor');
const projectId = new URLSearchParams(location.search).get('project');

if (!root || !projectId) throw new Error('Editor root or project ID is missing');

const response = await fetch(`/api/projects/${encodeURIComponent(projectId)}`, {
  credentials: 'same-origin',
  headers: { Accept: 'application/json' }
});
if (!response.ok) throw new Error(`Could not load project (${response.status})`);
const project = await response.json();

const editor = await mountEditor(root, {
  projectData: project.editorData,
  onChange: (editorData) => queueSave(projectId, editorData)
});

async function queueSave(id, editorData) {
  // Debounce frequent editor events in production; send data to your application API.
  const save = await fetch(`/api/projects/${encodeURIComponent(id)}`, {
    method: 'PUT',
    credentials: 'same-origin',
    headers: {
      'Content-Type': 'application/json',
      'X-CSRF-Token': window.csrfToken
    },
    body: JSON.stringify({ editorData })
  });
  if (!save.ok) throw new Error(`Could not save project (${save.status})`);
}
The page needs a mount element such as <div id="template-editor"></div>. The placeholder is not a claim about the SDK’s actual method names. Follow the selected SDK’s current quickstart for package installation, initialization, and the format of project data. Keep your own API boundary even when the editor SDK offers a convenient storage integration.
4. Design template loading, saving, and authorization
Define what is stored before wiring autosave. A typical application record includes an internal project ID, owner or tenant ID, template version or source ID, editor project data, timestamps, and a revision used to detect conflicting writes. Store the editor data in the format the SDK expects, but keep ownership and product permissions in your application database.
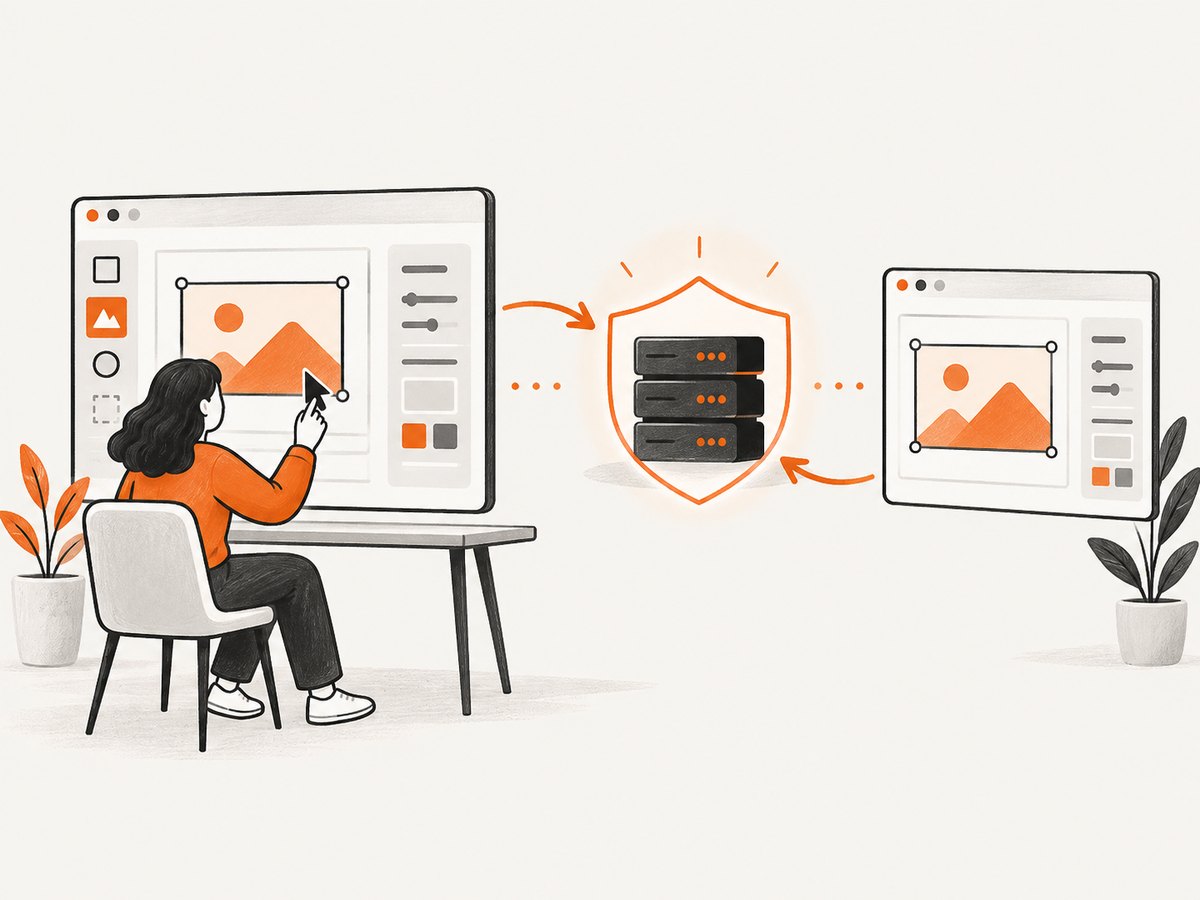
- Load through your backend. Resolve the signed-in user, check access to the requested project, then return only the project data that user may read.
- Save through your backend. Re-check authorization on every save. Do not trust a client-supplied project ID or user identity by itself.
- Handle duplicates deliberately. Decide whether duplication copies only the project data or also assets, permissions, and version history.
- Choose a conflict policy. Use revisions, optimistic concurrency, or another explicit rule so two tabs or collaborators do not silently overwrite each other.
- Keep private credentials server-side. GrapesJS template guidance describes custom loading and advises keeping private Platform API calls on the backend rather than exposing a private key in browser requests.
Use the editor’s documented template and project interfaces rather than treating a rendered HTML string as the entire editable state. A rendered result can omit editor-specific structure needed to resume editing. Verify that save, reload, duplicate, and export preserve the user’s intended content.
5. Build an app inside another editor platform
When your app runs inside a platform such as Canva, that platform owns the host page and its iframe. Your code can use only the documented APIs, permissions, and resources the platform makes available; it cannot assume unrestricted access to the design document or browser environment.
- Follow the platform’s app setup and request-verification rules.
- Use its documented APIs for document operations, identity, and user context.
- Verify tokens and backend requests according to the platform’s security guidance.
- Configure the backend to permit only required browser origins and methods.
- Test in the actual platform iframe. Its content security policy and available permissions may differ from a normal page.
Canva’s documentation describes its apps as JavaScript running inside an iframe, with access governed by its platform APIs and iframe environment. It also documents restrictive CSP behavior for the app iframe, including restrictions on some third-party scripts, nested browsing contexts, and external stylesheets. These are Canva host constraints; do not assume another host uses the same policy. Canva app model · Canva content security policy
6. Set browser boundaries and secure user content
Review the host and embedded service policies together. A page’s frame-src policy controls which frames it can load; an embedded page’s frame-ancestors policy controls which sites may frame it. Also check script and style policies, cookies, storage, permissions, CORS, and any required network destinations. A browser console CSP error usually identifies the blocked directive and resource.
Cross-origin requests from a browser need the receiving server to allow the requesting origin and method. Configure the narrowest CORS policy that supports your deployment. Do not put long-lived private API keys in frontend code, local storage, or logs. Use server-side credentials and short-lived, narrowly scoped tokens when a vendor supports them.
Treat imported HTML, CSS, iframe URLs, and user-authored embeds as untrusted input. Validate accepted formats on the server and define a deliberate policy for scripts, navigation, and external resources. If rendered content must be isolated, use a sandboxed iframe with only the permissions the feature needs. TinyMCE’s security guide cautions that client-side filtering can be bypassed and documents iframe sandboxing and safer handling of unsafe embeds. CKEditor’s HTML embed documentation also describes the security implications of embedding HTML. TinyMCE security guide · CKEditor HTML embed
7. Test the complete workflow
- Load a new template, edit it, save, reload, and confirm fidelity.
- Try expired sessions, unauthorized project IDs, and revoked access.
- Test two tabs or users saving around the same time.
- Test slow networks, API timeouts, retries, and interrupted uploads.
- Check production CSP, CORS, and iframe behavior on the actual deployment origin.
- Test keyboard navigation, focus behavior, screen reader labels, zoom, and small viewports.
- Test exports and confirm that external assets, fonts, and embeds behave as expected.
- Verify imported content cannot run disallowed scripts or escape its intended frame.
The results depend on your chosen SDK, host platform, browser, and deployment configuration. Documentation establishes available integration surfaces and constraints; it does not establish that a particular combination will work without testing.
8. Troubleshooting common integration failures
| Symptom | Likely cause | What to check or change |
|---|---|---|
| Editor does not appear | SDK initialization failed, mount node is missing, or a required resource was blocked. | Check the browser console and network panel, mount after the element exists, and verify the vendor’s supported runtime and setup. |
| Editor appears blank inside an iframe | Host or embedded page framing policy, CSP, or platform permissions prevent it from loading. | Inspect CSP and frame errors on both sides. Use the platform’s documented iframe workflow and test the production origin. |
| API call fails only in the browser | CORS preflight or allowed-origin configuration is missing or too narrow. | Check the preflight response, allowed origin, method, and headers; permit only the origins the app needs. |
| Save returns 401 or 403 | Session or token expired, CSRF check failed, or project authorization was denied. | Refresh authentication as appropriate, include the required CSRF token, and verify access on the server for that project. |
| Changes disappear after reload | Editor change events are not persisted, save requests fail, or the load path reads different data. | Track save status, inspect the request and response, and verify the same project record and editor data format are used both ways. |
| One user’s save overwrites another | Concurrent writes have no conflict detection. | Add a revision or version check and show a conflict or merge path rather than silently accepting stale writes. |
| Published design shows access prompt | Sharing or access settings restrict the design. | Review the publisher’s current sharing and embed settings; verify the design is available to intended viewers. |
| Imported content behaves unexpectedly | Unsupported markup, blocked resources, sanitization, or frame sandbox restrictions affect it. | Document accepted content, validate on the server, and test with the same sandbox and resource policy used in production. |
9. Performance, reliability, and cost
Performance
Editor startup, project size, asset loading, and export work all affect perceived responsiveness. Measure these in your own app rather than relying on a generic benchmark. Load only the project needed for the current editing session, avoid sending large unchanged assets with every save, and debounce rapid change events. If assets are uploaded separately, make upload progress and failure states visible. Test on the network conditions and devices your users rely on.
Reliability
Make persistence state clear: saving, saved, and save failed should not look the same. Retry transient requests carefully, make save operations safe to repeat where practical, and avoid treating an editor’s in-memory state as durable storage. A page refresh, expired session, or SDK exception should not silently discard edits; decide whether to preserve a local recovery draft and how it is reconciled with the server.
Cost and portability
Compare SDK pricing and license terms with hosting, storage, support, and engineering maintenance for a custom editor. The reviewed documentation establishes that GrapesJS Studio SDK is an embeddable option and documents template configuration; it does not settle licensing, supported framework scope, commercial terms, or your total operating cost. Confirm those directly with the vendor. Keep a migration plan for project data and assets, and periodically test whether you can export or transform them independently of the editor.
Or skip the browser setup
If the task is capturing a finished page while you build or validate your template workflow, ScreenshotNeo is a website screenshot API and MCP server. It does not embed an editor; it returns a screenshot or PDF from one request. See the API documentation.
curl -G "https://api.screenshotneo.com/v1/shot" -d access_key=YOUR_API_KEY --data-urlencode url=https://stripe.com -o shot.webpimport requests
r = requests.get("https://api.screenshotneo.com/v1/shot", params={"access_key": "YOUR_API_KEY", "url": "https://stripe.com"}, timeout=90)
open("shot.webp", "wb").write(r.content)const q = new URLSearchParams({ access_key: 'YOUR_API_KEY', url: 'https://stripe.com' });
const res = await fetch(`https://api.screenshotneo.com/v1/shot?${q}`);ScreenshotNeo accepts cookie and consent banners before capture and removes more than 60 known consent platforms, newsletter popups, and chat widgets; each step can be turned off. Bot checks, blank pages, timeouts, failed loads, and cache hits are not billed, and response headers report the page verdict and billing status. Its MCP server provides screenshot, page-info, and PDF tools for Claude, Cursor, and other MCP clients. The free plan includes 1,000 screenshots per month with no card; paid plans start at $5 for 3,000 shots. Sign up free for 1,000 screenshots a month, no card required.
Frequently asked questions
Can I embed Canva’s editor in my own SaaS?
Canva’s documented app model is for apps hosted inside Canva, using its iframe and exposed APIs. For an editable canvas in your own product, evaluate an embeddable editor SDK or build an editor; for a finished design, use Canva’s published-design embed workflow.
Does an iframe automatically make embedded HTML safe?
No. Use server-side validation and a deliberate sandbox and permission policy. A frame boundary is one control, not a replacement for safe content handling.
Should I store the final HTML or the editor project?
Store the data needed to reopen and edit the project in the format the chosen editor documents. Store exports separately when your product needs a rendered artifact, and test that both can be regenerated or recovered.
Can a published design embed be edited by visitors?
A published-design embed is for displaying a design. Editing permissions and workflows belong to the publishing platform and its sharing model; do not treat a view embed as an editor SDK.


