How to Enable TLS 1.3 in Apache, Nginx, and Cloudflare
Enable TLS 1.3 safely in Apache, Nginx, or Cloudflare, preserve compatibility, avoid early-data risks, and verify the protocol your clients negotiate.
TLS 1.3 is enabled differently depending on where HTTPS terminates. On Apache, configure SSLProtocol and use Apache 2.4.43 or newer with OpenSSL 1.1.1 or newer. On Nginx, configure ssl_protocols in an HTTPS server block and make sure the build includes ngx_http_ssl_module linked to a TLS 1.3-capable OpenSSL. On Cloudflare, enable TLS 1.3 at the edge under SSL/TLS → Edge Certificates or set the zone’s tls_1_3 value through the API.
Most sites should keep TLS 1.2 enabled alongside TLS 1.3 during rollout:
# Apache
SSLProtocol TLSv1.2 TLSv1.3

# Nginx
ssl_protocols TLSv1.2 TLSv1.3;
Use a TLS-1.3-only policy only after you have checked every browser, API client, monitoring probe, partner integration, and device that must connect. TLS 1.3 at Cloudflare and TLS between Cloudflare and your origin are separate connections, so verify both legs.
What you need before enabling TLS 1.3
| Platform | Where TLS terminates | Required support | Main setting |
|---|---|---|---|
| Apache | Apache’s mod_ssl |
Apache 2.4.43+ and OpenSSL 1.1.1+ | SSLProtocol TLSv1.2 TLSv1.3 |
| Nginx | Nginx HTTP SSL module | --with-http_ssl_module and TLS 1.3-capable OpenSSL |
ssl_protocols TLSv1.2 TLSv1.3; |
| Cloudflare | Cloudflare’s edge | A Cloudflare zone with the TLS 1.3 control available | Dashboard switch or tls_1_3=on |
Apache’s project guidance says Apache HTTP Server 2.4.43 or newer is required to operate a TLS 1.3 web server with OpenSSL 1.1.1. The Apache mod_ssl documentation defines SSLProtocol and its accepted protocol versions.
Nginx’s HTTP SSL module documentation describes the module build requirement and the ssl_protocols directive. Nginx’s HTTPS configuration guide shows the certificate, key, and HTTPS listener together.
For Cloudflare, the TLS 1.3 documentation covers the dashboard control and the on, zrt, and off API values.
Enable TLS 1.3 in Apache
1. Confirm Apache and OpenSSL versions
apachectl -v
openssl version
You need Apache 2.4.43 or later and OpenSSL 1.1.1 or later for TLS 1.3 web serving. Package names vary by operating system, so upgrade through your distribution’s supported repositories or your managed image process rather than copying binaries between systems.
2. Confirm that mod_ssl is loaded
apachectl -M | grep sslThe output should include ssl_module. If it is absent, enable or install the distribution’s SSL module and restart the configuration process. The exact command differs between Debian-based, RHEL-based, and vendor-managed systems.
3. Add the protocol policy to the HTTPS virtual host
<VirtualHost *:443>
    ServerName example.com

    SSLEngine on
    SSLCertificateFile /etc/letsencrypt/live/example.com/fullchain.pem
    SSLCertificateKeyFile /etc/letsencrypt/live/example.com/privkey.pem

    SSLProtocol TLSv1.2 TLSv1.3
</VirtualHost>
SSLProtocol can be placed in server configuration or a virtual-host context. Keeping TLS 1.2 gives older clients a compatible protocol while allowing capable clients to negotiate TLS 1.3. For a controlled TLS-1.3-only deployment, use:
SSLProtocol TLSv1.3On name-based virtual hosts, Apache 2.4.42 and later can honor each virtual host’s protocol setting when built with OpenSSL 1.1.1 or later and the client supplies SNI. If clients do not send SNI, the default virtual host can determine the result.
4. Validate and reload safely
apachectl configtest
sudo systemctl reload apache2
Some distributions use httpd instead of apache2. Always run the configuration test before reloading. A reload lets existing connections finish while the new workers use the updated policy.
Enable TLS 1.3 in Nginx
1. Check the binary and linked OpenSSL
nginx -V 2>&1
openssl version
Inspect the nginx -V output for --with-http_ssl_module. The module is not built by default. The linked OpenSSL library must support TLS 1.3; a newer Nginx binary alone cannot add TLS 1.3 when its library does not.
2. Configure the HTTPS server block
server {
    listen 443 ssl;
    server_name example.com;

    ssl_certificate     /etc/letsencrypt/live/example.com/fullchain.pem;
    ssl_certificate_key /etc/letsencrypt/live/example.com/privkey.pem;

    ssl_protocols TLSv1.2 TLSv1.3;

    location / {
        proxy_pass http://app_backend;
    }
}
The important pieces are the TLS listener, certificate, private key, and ssl_protocols. Recent Nginx releases, including 1.27.3 and later, default to TLS 1.2 and TLS 1.3 when the linked OpenSSL supports them. Declaring the directive explicitly makes the intended policy visible and avoids surprises after an upgrade.
3. Test before reloading
sudo nginx -t
sudo systemctl reload nginx
If the syntax test reports an unknown directive, check that the SSL module is present and that you are editing the configuration actually loaded by the running binary. If it reports a certificate error, verify both paths and file permissions.
Early data and replay protection
Nginx supports TLS 1.3 early data with ssl_early_data on; when OpenSSL 1.1.1 or newer is available. Nginx documents that requests sent within early data are subject to replay attacks. Do not enable it simply because TLS 1.3 is enabled. If your application needs early data, pass the $ssl_early_data value upstream and reject or safely handle non-idempotent requests such as payments, account changes, and state-changing API calls.
Enable TLS 1.3 in Cloudflare
Dashboard method
- Open the Cloudflare dashboard for the zone.
- Go to SSL/TLS → Edge Certificates.
- Find TLS 1.3 and switch it to On.
- Allow configuration propagation, then verify from a TLS 1.3-capable client.
Cloudflare documents TLS 1.3 for Free, Pro, Business, and Enterprise plans. The edge control does not expose individual TLS 1.3 cipher selection; Cloudflare applies the relevant TLS 1.3 cipher suites automatically. Cipher controls for TLS 1.0–1.2 are a separate setting.
API values
The zone setting is named tls_1_3. Cloudflare documents these values:
| Value | Meaning |
|---|---|
on |
Serve TLS 1.3 when the connecting client supports it. |
zrt |
Enable TLS 1.3 with Zero Round Trip Time resumption. |
off |
Disable TLS 1.3 at the Cloudflare edge. |
Use the value that matches your rollout policy. Zero Round Trip Time resumption can reduce handshake latency, but any design that accepts early data must account for replay. Keep TLS 1.2 available unless you have measured the compatibility impact of raising the minimum protocol.
Do not forget the origin connection
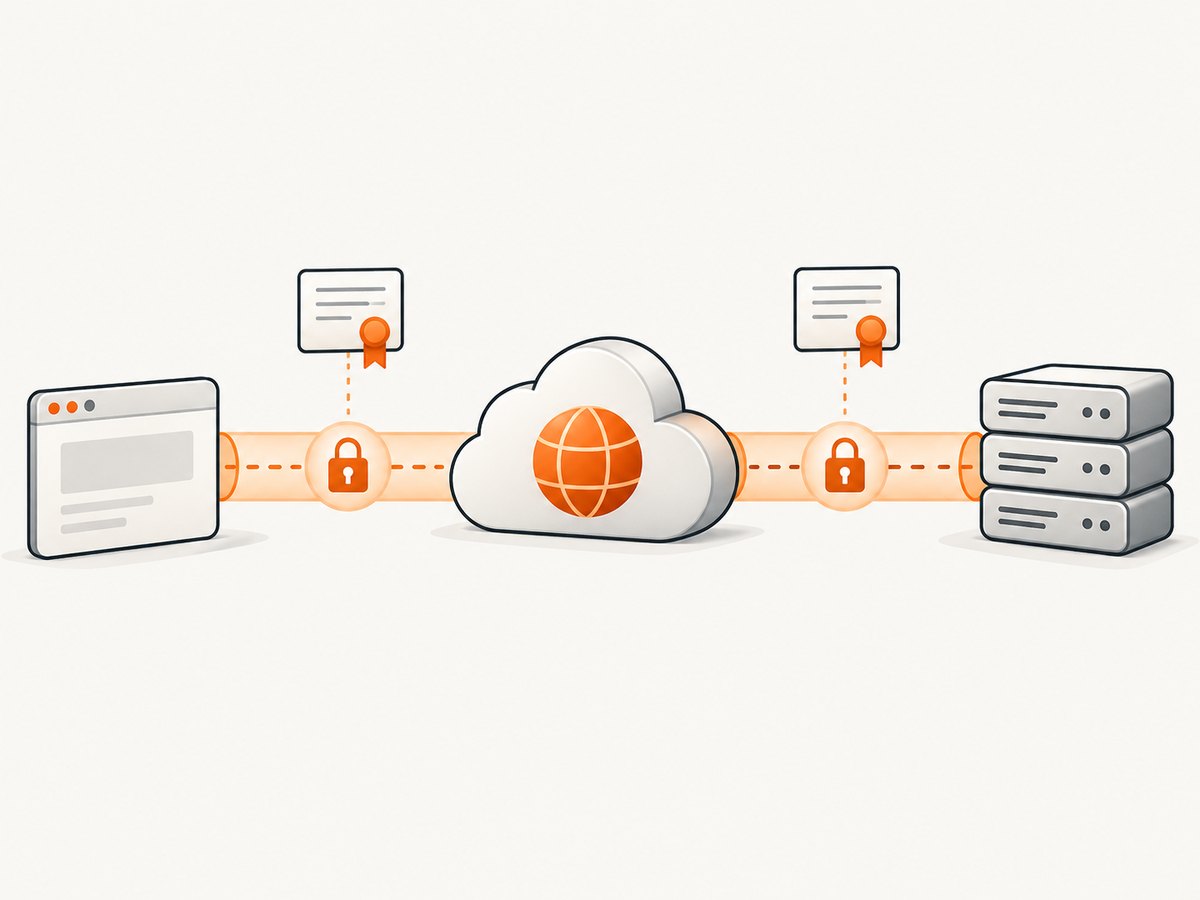
Cloudflare termination is only the client-to-edge leg. Your origin still needs a valid certificate, port 443, and a working HTTPS configuration. A browser can negotiate TLS 1.3 with Cloudflare while Cloudflare-to-origin fails because Apache or Nginx has an expired certificate, an unsupported protocol, or a firewall rule blocking 443.
Cloudflare’s encryption guidance recommends strengthening the deployment with a minimum TLS version, HSTS, and TLS 1.3. Enable HSTS only after HTTPS is fully working and tested; an incorrect HSTS rollout can make recovery harder for visitors and subdomains.
How to verify that TLS 1.3 is actually being used
Inspect a direct handshake
openssl s_client \
  -connect example.com:443 \
  -servername example.com \
  -tls1_3 < /dev/null
Look for the negotiated protocol line in the output. It should report Protocol: TLSv1.3. The -servername option matters on SNI-based virtual hosting because it selects the intended certificate and virtual host.
Inspect the normal client path
curl -I -v https://example.com/Verbose output helps identify certificate-chain errors, redirects, handshake failures, and which hostname answered. A successful request alone does not prove TLS 1.3; use a protocol-aware diagnostic such as openssl s_client or your client’s TLS inspection facilities.
Check both sides of Cloudflare
- Test the public Cloudflare hostname.
- Test the direct origin hostname when it is intentionally exposed for administration or diagnostics.
- Compare the negotiated protocol and certificate on each connection.
- Repeat after certificate renewal, web-server upgrades, OpenSSL upgrades, or Cloudflare setting changes.
Compatibility choices and rollout strategy
TLS 1.3 removes older protocol behavior and changes the handshake and cipher negotiation. The practical compatibility choice is usually to serve TLS 1.2 and TLS 1.3 together, then monitor clients before raising the minimum. Cloudflare’s protocol guidance generally recommends TLS 1.3 for best security, while also documenting limitations involving older clients and integrations.
- Inventory clients, partner systems, health checks, and embedded devices.
- Upgrade Apache, Nginx, and OpenSSL where required.
- Enable
TLSv1.2 TLSv1.3and verify representative clients. - Check logs for handshake failures and protocol-version alerts.
- Only then consider TLS 1.3-only settings or a higher minimum TLS control at Cloudflare.
- Roll back the protocol setting if a critical integration cannot connect, then schedule that client’s upgrade.
Performance, reliability, and cost notes
TLS 1.3 can reduce handshake round trips for new connections and offers a simpler modern protocol design, but the visible result depends on network distance, connection reuse, HTTP version, session resumption, and application response time. Do not treat enabling TLS 1.3 as a substitute for keep-alive, HTTP/2 or HTTP/3 tuning, certificate-chain optimization, or backend performance work.
Keep early data disabled unless you have a clear idempotency design. A replay-safe GET may be suitable in some architectures; a purchase, password change, or transfer is not safe merely because it arrived through TLS 1.3.
The configuration itself has no per-request software charge when you run Apache or Nginx, but upgrades, certificate management, monitoring, and incident response still consume operational time. Cloudflare pricing and plan behavior should be checked in the current Cloudflare account because the TLS 1.3 control is a hosted edge feature.
Troubleshooting common TLS 1.3 problems
| Symptom | Likely cause | Fix |
|---|---|---|
SSLProtocol or ssl_protocols is unknown |
SSL module is missing or the configuration is being read by a different binary. | Check Apache modules or nginx -V; install or rebuild with SSL support. |
| TLS 1.3 is absent from handshake output | Old OpenSSL library, old server package, or a proxy terminates TLS elsewhere. | Inspect the linked OpenSSL version and test the actual TLS terminator. |
| Apache will not start after editing | Syntax error, invalid certificate path, or unsupported protocol on the installed OpenSSL. | Run apachectl configtest, correct the reported line, and verify versions. |
| Nginx reload fails | Invalid syntax, unreadable key, or certificate/key mismatch. | Run nginx -t, check permissions, and verify the certificate and key pair. |
| Cloudflare shows TLS 1.3 but origin requests fail | Client-to-edge works while edge-to-origin has a certificate, port, firewall, or protocol problem. | Test the origin independently and inspect Cloudflare origin connection errors. |
| Some old clients cannot connect | TLS 1.2 or older compatibility was removed. | Restore TLS 1.2, identify the affected clients, and upgrade them before tightening policy. |
| State-changing requests behave unexpectedly with early data | Replayable 0-RTT data was accepted without application safeguards. | Disable early data or reject non-idempotent requests when $ssl_early_data is set. |
| The wrong certificate appears | SNI was omitted or the request reached a default virtual host. | Use -servername with OpenSSL and verify the hostname and virtual-host order. |
Or skip the browser setup
If your goal is to capture a page after changing TLS settings, ScreenshotNeo can return a screenshot or PDF with one GET request. It accepts PNG, JPEG, WebP, and PDF output, and its capture options include custom headers, cookies, user agents, waiting rules, full-page loading, and caching. Cookie banners, newsletter popups, and chat widgets are removed before the shot. Bot checks, blank pages, timeouts, failed loads, and cache hits are not billed, and the response identifies the result with X-Page-Verdict and X-Billed headers. An MCP server provides take_screenshot, get_page_info, and capture_pdf tools for Claude, Cursor, and other MCP clients.
See the ScreenshotNeo documentation for all options.
cURL
curl -G "https://api.screenshotneo.com/v1/shot" -d access_key=YOUR_API_KEY --data-urlencode url=https://stripe.com -o shot.webpPython
import requests
r = requests.get("https://api.screenshotneo.com/v1/shot", params={"access_key": "YOUR_API_KEY", "url": "https://stripe.com"}, timeout=90)
open("shot.webp", "wb").write(r.content)
Node.js
const q = new URLSearchParams({ access_key: 'YOUR_API_KEY', url: 'https://stripe.com' });
const res = await fetch(`https://api.screenshotneo.com/v1/shot?${q}`);
Every plan includes every feature. The free plan includes 1,000 screenshots per month with no card; paid plans start at $5 for 3,000. Create a free ScreenshotNeo account.
FAQ
Can I enable only TLS 1.3?
Yes. Apache can use SSLProtocol TLSv1.3, and Nginx can use ssl_protocols TLSv1.3;. Do this only after confirming that all required clients and integrations support TLS 1.3.
Does enabling TLS 1.3 automatically enable HTTP/2?
No. TLS protocol selection and HTTP protocol negotiation are separate configuration concerns.
Does Cloudflare TLS 1.3 protect my origin automatically?
No. It controls the Cloudflare edge connection. Configure and verify HTTPS separately on the Apache or Nginx origin.
Do I need to select TLS 1.3 cipher suites?
Apache and Nginx use the TLS library’s TLS 1.3 behavior. Cloudflare does not expose individual TLS 1.3 cipher selection in its zone control.
How often should I recheck the configuration?
Recheck after certificate renewal, operating-system or web-server upgrades, OpenSSL changes, Cloudflare setting changes, and any report from a client that cannot connect.


