How to Use Nmap for Vulnerability Scanning
Learn how to use Nmap and NSE scripts for authorized vulnerability checks, validate findings, avoid risky scans, and build a safer workflow.
Direct answer: Use Nmap to discover authorized hosts, ports, and service versions, then run carefully selected Nmap Scripting Engine (NSE) scripts for known vulnerability checks. Nmap is not a complete vulnerability-management platform. Its results are leads that require validation against the service, vendor advisories, configuration, and—when appropriate—a dedicated scanner.
Nmap describes itself as a network exploration and security auditing utility. The Nmap Project also states that “while Nmap isn’t a comprehensive vulnerability scanner, NSE is powerful enough to handle even demanding vulnerability checks.” Read the official NSE chapter and NSE usage guide before scanning production systems.
1. Get authorization and define scope
Only scan systems you own or have explicit permission to assess. Record the exact IP addresses or hostnames, permitted ports, scan window, source address, rate limits, and an escalation contact. A publicly reachable host is not automatically fair game. The Nmap Project’s legal guidance advises requesting permission even before a light scan.
- Write down the target list. Prefer an inventory file over a broad CIDR range when possible.
- Separate development, staging, and production targets.
- Confirm whether intrusive, brute-force, exploit, or denial-of-service checks are prohibited.
- Agree on how to handle fragile devices, industrial systems, and rate-sensitive services.
- Capture the Nmap version, date, operator, source network, and command line for every run.
2. Install Nmap and inspect available scripts
Install Nmap from your operating system’s trusted package source or the official download page. Verify the installation:
nmap --version
nmap --script-updatedb
NSE scripts are normally installed in Nmap’s scripts directory. List scripts and search their documentation locally:
nmap --script-help vuln
nmap --script-help ssl-enum-ciphers
nmap --script-help http-security-headers
Read each script’s documentation, source, categories, arguments, and prerequisites. NSE scripts are not sandboxed. Third-party scripts should be trusted or audited before use.
3. Discover hosts and exposed services first
Script execution is commonly paired with a port scan because scripts can depend on discovered port states and service detection. Start with a low-impact inventory scan in an approved environment:
nmap -sV --top-ports 100 -oA inventory 192.0.2.10-sVprobes services to identify product and version information.--top-ports 100limits the first pass to common ports. Use an explicit-plist when your scope requires more precision.-oA inventorywrites normal, XML, and grepable output with a shared filename prefix.
For a host-discovery pass over an approved subnet, use:
nmap -sn -n 192.0.2.0/24 -oA hosts-sn performs host discovery without a port scan, while -n skips reverse DNS lookups. Firewalls and filtered networks can make discovery incomplete, so compare results with your asset inventory.
4. Choose NSE scripts deliberately
The --script option accepts individual scripts, expressions, or categories. -sC selects the default script set; it is not the same as a vulnerability scan. For a documented, targeted check:
nmap -sV -p 443 --script ssl-enum-ciphers -oA tls-check 192.0.2.10For a small, authorized lab target where you have reviewed the scripts, select the vulnerability category:
nmap -sV -p 80,443 --script vuln -oA web-vuln 192.0.2.10Do not treat vuln as universally safe or complete. Inspect the individual scripts that will run and remove checks that are unsuitable for the target. Categories include:
| Category | Meaning and caution |
|---|---|
safe |
Designed to avoid destructive behavior, but still review target impact. |
vuln |
Checks for known weaknesses; a result still needs validation. |
intrusive |
May affect services or consume significant resources. |
exploit |
Attempts exploitation. Use only under explicit authorization. |
dos |
Can cause denial of service. Avoid unless a written test plan permits it. |
Never use --script all as a beginner shortcut. It can include dangerous scripts, including intrusive, exploit, brute-force, and denial-of-service behavior.
5. Useful scan options and examples
Limit ports and hosts
nmap -sV -p 22,80,443 --script vuln 192.0.2.10
nmap -sV -p- --script ssl-enum-ciphers 192.0.2.10
nmap -iL approved-targets.txt -p 443 --script ssl-enum-ciphers
-p- scans all TCP ports and can be considerably slower. An explicit port list is easier to explain and less disruptive.
Control timing and retries
nmap -sV -T2 --max-retries 2 --host-timeout 5m --script vuln 192.0.2.10Conservative timing such as -T2 reduces load. More aggressive timing can shorten a scan but increases packet rate and the chance of dropped probes or service impact. --max-retries and --host-timeout prevent a single unreliable target from consuming the entire window.
Use transport and discovery controls carefully
nmap -sS -Pn -n -p 443 --script ssl-enum-ciphers 192.0.2.10-sSrequests a TCP SYN scan and generally requires elevated privileges.-Pnskips host discovery and treats targets as online; use it when discovery probes are blocked, but expect scans of offline addresses.-navoids DNS lookups and can improve speed and repeatability.
Choose options based on the agreed test plan. There is no universally safe command for every network.
Pass script arguments only when documented
nmap --script-help http-enum
nmap -p 80 --script http-enum --script-args http-enum.basepath=/app 192.0.2.10
Argument names and behavior vary by script. Copying an argument from an unrelated example can produce misleading results or unexpected traffic.
6. Save, parse, and review results
NSE output is integrated into normal and XML output. Save both human-readable and machine-readable records:
nmap -sV -p 80,443 --script vuln -oN report.txt -oX report.xml 192.0.2.10Keep the target scope, command, Nmap version, timestamps, and scan conditions beside the output. Review:
- Whether the host and port were actually reachable.
- Which service and version Nmap identified, and how confident that identification is.
- The exact script name and evidence it reported.
- Whether a finding is a detection, a version-based inference, or an exploit attempt.
- Whether the service configuration or compensating controls change the risk.
Confirm suspected issues with vendor advisories, package inventories, configuration review, or a controlled verification step. A script result alone does not prove exploitability or establish complete coverage.
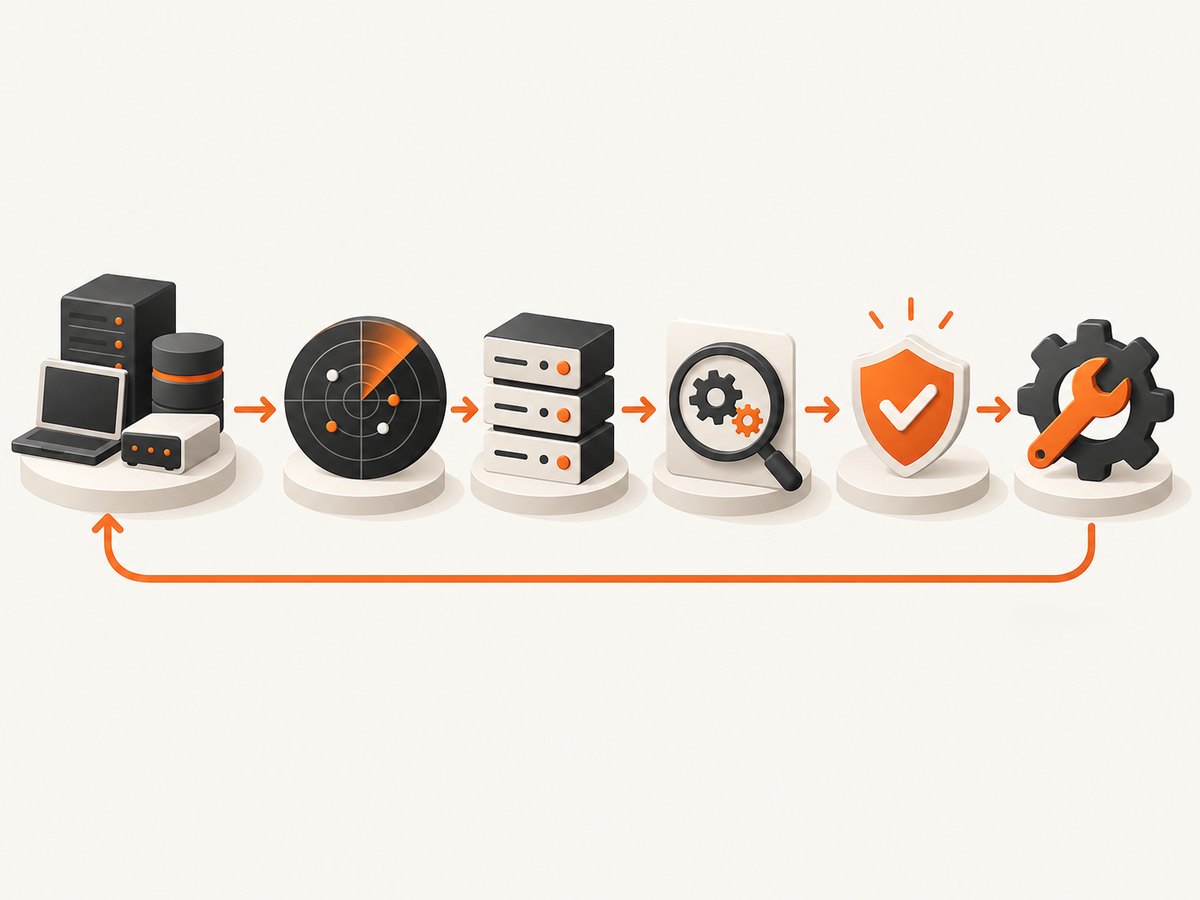
7. Build a repeatable vulnerability workflow
- Scope: obtain written authorization and an asset list.
- Baseline: discover hosts, ports, and services with a low-impact scan.
- Select: map services to specific, documented NSE scripts.
- Run: scan during the approved window with conservative timing.
- Record: save XML and normal output plus command metadata.
- Validate: confirm versions, advisories, configuration, and exposure.
- Remediate: patch, reconfigure, segment, or otherwise address confirmed risk.
- Rescan: repeat the same focused check and compare results.
Use a dedicated vulnerability-management scanner or process when you need broad authenticated checks, host-level package inspection, prioritization, ownership, and remediation tracking. Nmap’s strength is transparent network discovery and scriptable checks, not a complete lifecycle.
8. Troubleshooting common errors
| Symptom | Likely cause | Fix |
|---|---|---|
| No hosts appear | Discovery probes are blocked or the range is wrong. | Confirm scope and routing; try -Pn for approved targets and compare with asset records. |
| Ports show filtered | A firewall drops probes. | Coordinate with the network owner, scan an approved vantage point, or document the limitation. |
| Script does not run | The required port or service was not discovered, or the script has prerequisites. | Run --script-help scriptname, specify the correct -p, and perform service detection. |
| Results are inconsistent | Rate limits, packet loss, load balancing, or changing services. | Use conservative timing, repeat during a stable window, and record scan conditions. |
| “Permission denied” | The selected scan requires privileges. | Use an authorized elevated execution context or choose a permitted unprivileged scan type. |
| A service becomes unstable | Version detection or an NSE script triggered fragile behavior. | Stop, notify the contact, remove intrusive checks, lower timing, and follow the incident plan. |
| A finding looks false positive | The script inferred risk from a banner or version. | Verify the installed patch level, backport status, configuration, and vendor guidance. |
9. Performance, reliability, and cost considerations
Performance: scanning all ports, large ranges, version detection, and many scripts multiply work. Narrow the target and port set first, then expand only when the evidence requires it. Conservative timing and bounded retries improve predictability.
Reliability: packet filtering, NAT, load balancers, DNS failures, rate limiting, and intermittent services can hide or distort results. Run from a network location that can legitimately reach the assets, preserve raw output, and repeat important checks.
Operational safety: Nmap documentation warns that version scanning and some NSE scripts can crash poorly written applications. Exclude fragile systems or obtain an explicit maintenance window.
Cost: Nmap is free and open source, but scanning still consumes operator time, bandwidth, test windows, and remediation effort. Budget for validation and follow-up rather than treating a single command as a complete assessment.
Or skip the browser setup
If your workflow also needs screenshots of dashboards, evidence pages, or remediation tickets, ScreenshotNeo provides a website screenshot API and MCP server. It is separate from Nmap: one GET request returns a PNG, JPEG, WebP, or PDF.
curl -G "https://api.screenshotneo.com/v1/shot" -d access_key=YOUR_API_KEY --data-urlencode url=https://stripe.com -o shot.webpimport requests
r = requests.get("https://api.screenshotneo.com/v1/shot", params={"access_key": "YOUR_API_KEY", "url": "https://stripe.com"}, timeout=90)
open("shot.webp", "wb").write(r.content)const q = new URLSearchParams({ access_key: 'YOUR_API_KEY', url: 'https://stripe.com' });
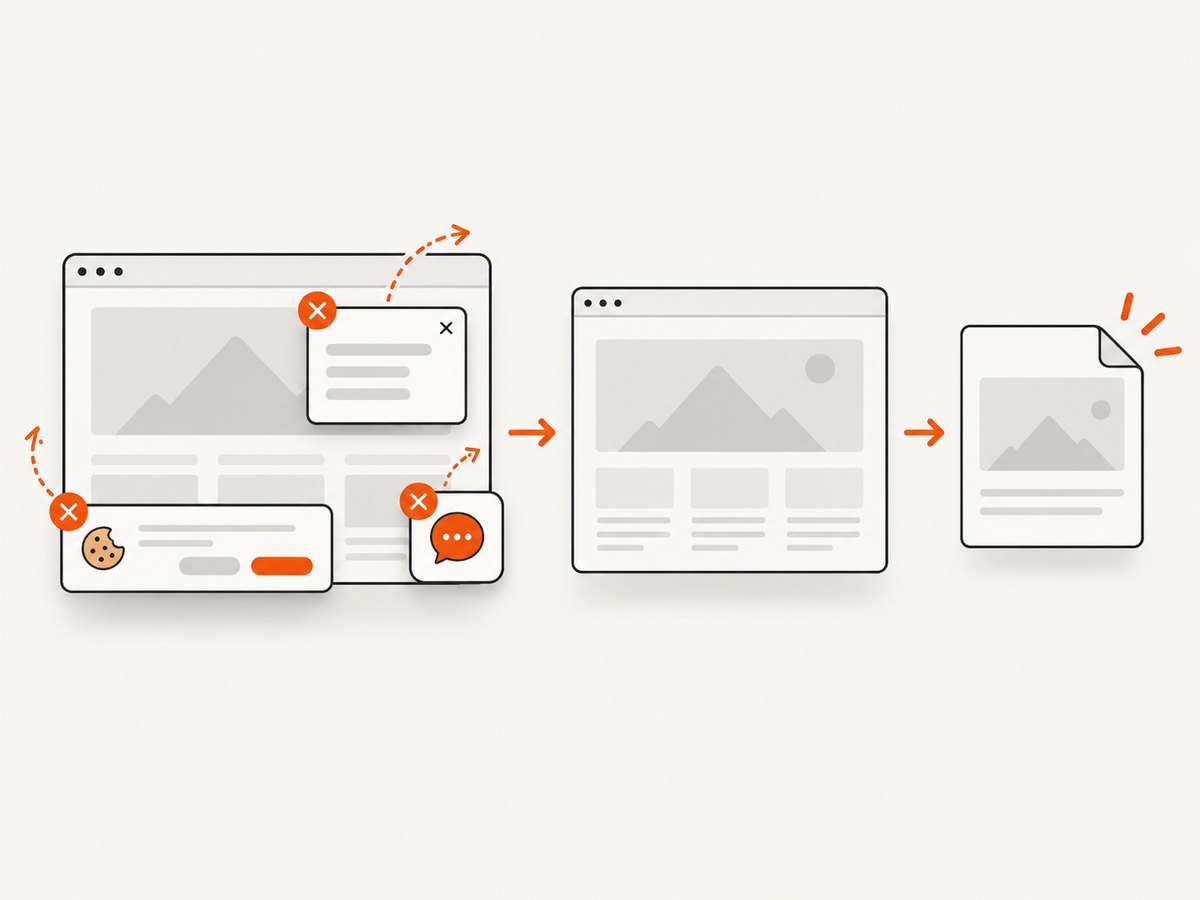
const res = await fetch(`https://api.screenshotneo.com/v1/shot?${q}`);See the ScreenshotNeo API documentation for request options. Cookie banners, newsletter popups, and chat widgets are removed before the shot. Bot checks, blank pages, timeouts, failed loads, and cache hits are not billed, and response headers identify the page verdict and billing status. Its MCP server includes take_screenshot, get_page_info, and capture_pdf for Claude, Cursor, and other MCP clients. The Free plan includes 1,000 screenshots per month with no card; paid plans start at $5 for 3,000 screenshots. Create a free ScreenshotNeo account.
FAQ
Does --script vuln find every vulnerability?
No. It runs available scripts in that category and depends on discovered services and script coverage. Validate results and use broader tools when comprehensive coverage is required.
Is -sC a vulnerability scan?
No. It selects the default NSE scripts. Review those scripts and choose vulnerability checks deliberately.
Can I scan a public website without asking?
No. Obtain authorization and follow the owner’s testing rules. Public reachability is not permission.
Why did Nmap miss a service?
Filtering, an incomplete port list, host discovery failure, rate limiting, or a service that was unavailable during the scan can all contribute. Check scope, routing, ports, and repeatability.
Where should I learn more?
Use the Nmap Project’s introduction, NSE usage guide, legal guidance, and the official Nmap Network Scanning book contents.


