What Is a SAN Certificate and How to Create One with OpenSSL
Learn what a SAN certificate contains, create a SAN-enabled CSR with OpenSSL, and verify that the issued certificate covers every name clients use.
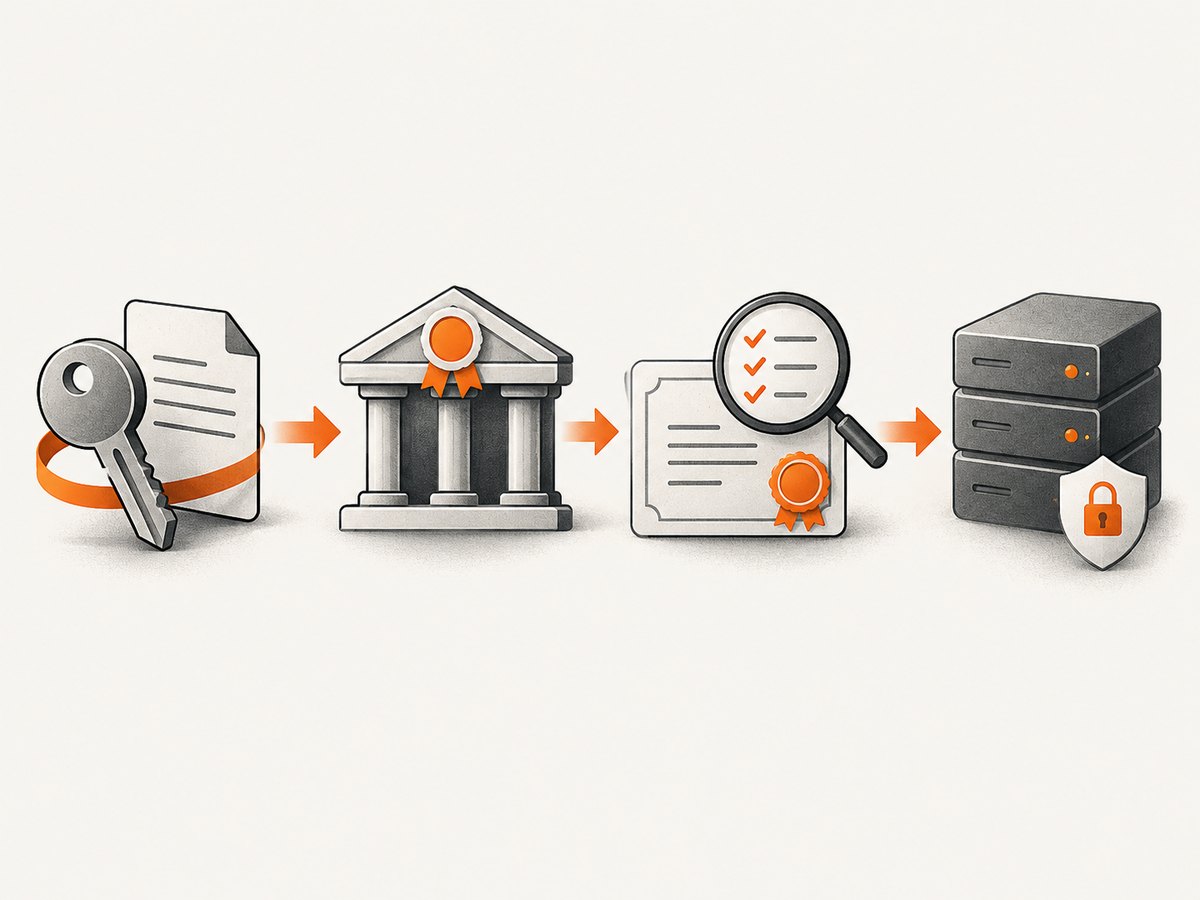
A SAN certificate is an X.509 certificate whose subjectAltName extension lists the identities it covers, such as DNS hostnames or IP addresses. To request one with OpenSSL, put each identity in the correct SAN type in a configuration file, generate a private key and CSR, submit the CSR to a certificate authority (CA), then inspect the issued certificate to confirm the names are present. The CA decides what it actually issues; a CSR is a request, not a guarantee.
This guide covers DNS names, IP addresses, and other SAN types, with runnable OpenSSL commands, verification steps, common failure fixes, and guidance for private testing versus publicly trusted certificates.
1. What a SAN certificate is
SAN stands for Subject Alternative Name. In X.509, subjectAltName is an extension containing one or more identities associated with the certificate. It lets a certificate identify multiple names, for example example.com and www.example.com, without requiring a separate certificate for each name. The extension is a sequence of typed values; the type matters. RFC 5280 defines DNS names, IP addresses, email addresses, URIs, and other GeneralName choices, and requires at least one entry when the extension is present. RFC 5280.
For HTTPS, include every hostname users or services will actually connect to. A certificate for example.com does not automatically cover www.example.com, an IP literal, or a different subdomain. The client checks the name it used against the certificate identities, in addition to checking certificate validity and trust.
2. Pick the right SAN type
| Identity | SAN type | OpenSSL config form | Example |
|---|---|---|---|
| Hostname or domain | dNSName |
DNS.n |
DNS.1 = example.com |
| IP address | iPAddress |
IP.n |
IP.1 = 192.0.2.10 |
| Email address | rfc822Name |
email.n |
email.1 = admin@example.com |
| URI | uniformResourceIdentifier |
URI.n |
URI.1 = https://example.com/service |
OpenSSL also supports other SAN forms such as registered IDs, directory names, and otherName; consult its X.509v3 configuration documentation when those specialized identity types are needed. A URI SAN must have a scheme and scheme-specific part. Do not put an IP literal in a DNS entry: DNS.1 = 192.0.2.10 requests a DNS name, not an IP SAN. The encoded type is defined by the standard, not inferred from how the value looks.
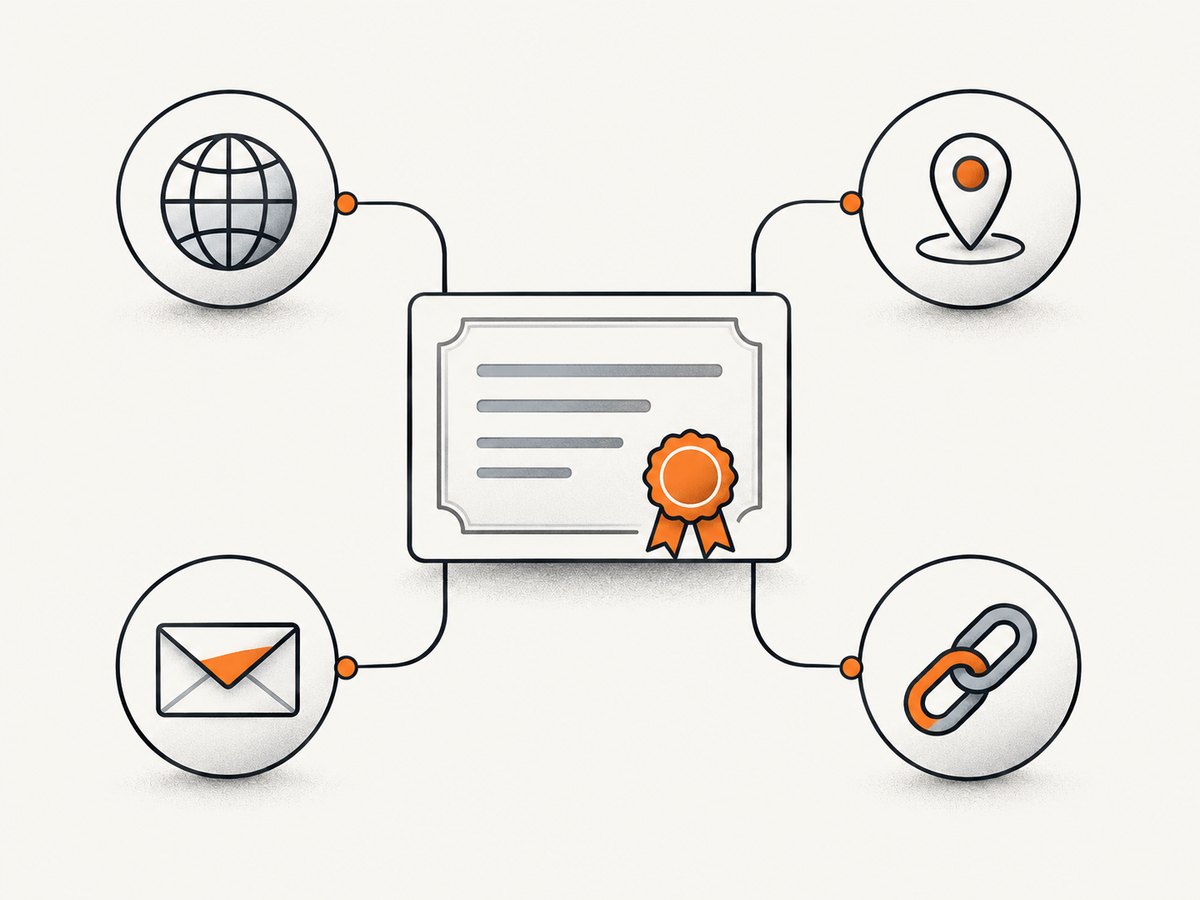
Wildcard names are subject to CA and client rules. If you need one, follow the issuing CA’s accepted syntax and validation policy, and inspect the issued result. Do not assume a wildcard covers the apex domain or arbitrary levels of subdomains.
3. Create a SAN request with OpenSSL
Step 1: Write a configuration file
Create san.cnf in a working directory. Replace the example organization and names with identities you control and need. The example requests two DNS names and one IPv4 address.
[req]
distinguished_name = req_distinguished_name
req_extensions = req_ext
prompt = no

[req_distinguished_name]
C = US
ST = State
L = City
O = Example Organization
CN = example.com

[req_ext]
subjectAltName = @alt_names

[alt_names]
DNS.1 = example.com
DNS.2 = www.example.com
IP.1 = 192.0.2.10
The CN (Common Name) is included as a distinguished-name field here, but list the actual identities in SAN and verify the CA’s output. Add further entries using consecutive indexes such as DNS.3 or IP.2. Use IP.n for IPv4 or IPv6 literals; do not use a port number as part of an IP SAN.
Step 2: Generate a private key and CSR
For a broadly compatible example, generate a 2048-bit RSA key and a certificate signing request:
openssl req -new -newkey rsa:2048 -nodes \
  -keyout example.key \
  -out example.csr \
  -config san.cnf \
  -reqexts req_ext
-new creates a request, -newkey rsa:2048 creates the private key, -keyout writes that key, -out writes the CSR, -config selects the configuration, and -reqexts req_ext selects the section containing the requested extensions. OpenSSL documents these options in its req command reference.
The -nodes flag leaves the generated private key unencrypted on disk. It avoids an interactive passphrase prompt, which can be convenient for automation, but requires careful file permissions and secret handling. If you need an encrypted key, omit -nodes and supply a passphrase securely when prompted or through an appropriate secret-management workflow. Never put a production private key in source control or send it to the CA. The CSR contains the public key and requested details; the matching private key stays with you.
Step 3: Inspect the CSR before submitting it
openssl req -in example.csr -noout -textFind Requested Extensions and confirm the SAN list includes every required identity under the correct type. Then submit example.csr to your enterprise CA or chosen public CA, following its validation and enrollment process. A CA may require proof of control for each name and may apply its own issuance policy. It controls the final certificate contents and trust chain; the requested CSR extensions do not force it to copy every value. Microsoft’s overview likewise describes creating a SAN request and submitting it to an enterprise, standalone, or third-party CA: Microsoft SAN certificate guidance.
4. Self-sign only for private testing
For a lab or a private trust setup, OpenSSL can create a self-signed certificate from the same configuration. This command creates a temporary certificate and key; do not treat it as publicly trusted:
openssl req -new -x509 -nodes -days 30 \
  -keyout test.key \
  -out test-cert.pem \
  -config san.cnf \
  -extensions req_ext
OpenSSL’s -x509 option creates a self-signed certificate rather than an ordinary CSR. Browsers and operating systems will not automatically trust it merely because it contains SANs. For production public HTTPS, obtain issuance from a CA whose chain is trusted by the clients. For private services, distribute and manage trust in the relevant private CA or test environment according to that environment’s policy. See the OpenSSL req reference.
5. Inspect and verify the issued certificate
After receiving the certificate, inspect its SAN extension and its basic metadata:
openssl x509 -in issued-cert.pem -text -noout
openssl x509 -in issued-cert.pem -noout -subject -issuer -dates
In the first output, locate X509v3 Subject Alternative Name. Check every DNS name and IP address that clients will use, including alternate production hostnames, internal service names where relevant, and the exact IP if clients connect by IP. Confirm that names appear as the correct SAN type. The second command displays the subject, issuer, and validity dates. OpenSSL documents these inspection options in its x509 command reference.
Use this verification checklist before deployment:
- The SAN extension exists in the issued certificate.
- Each client-facing hostname is present as a DNS SAN.
- Each IP literal clients use is present as an IP SAN, not a DNS SAN.
- The certificate is within its validity dates and has the expected issuer.
- The deployed certificate and private key belong together, and the served chain is configured for the target clients.
Text inspection confirms contents; it does not by itself prove that a client trusts the issuer, that the server is presenting the right certificate, or that the private key matches. Check those separately in the actual deployment environment.
6. Troubleshooting common SAN problems
| Symptom | Likely cause | Fix |
|---|---|---|
| Hostname mismatch in a browser or client | The hostname used by the client is missing from SAN, or the certificate served is not the one inspected. | Add the exact DNS name to the request, obtain a reissued certificate, and verify the certificate actually served by the endpoint. |
| Connection by IP fails name verification | The address was placed under DNS.n or omitted. |
Request it with IP.n, have the CA issue it, and confirm it appears as an IP SAN. |
| SAN appears in CSR but not certificate | The CA controls issuance and did not include the requested extension. | Check the CA profile and request procedure; ask for an issuance profile that includes the approved SANs, then inspect the reissued certificate. |
| OpenSSL says it cannot find the extension section | The section name passed to -reqexts or -extensions does not match the configuration, or the wrong config file was loaded. |
Confirm the file path, section spelling, and that the section includes subjectAltName = @alt_names. |
| Configuration parses but a SAN is absent | An entry is misspelled, indexed unexpectedly, placed outside the referenced section, or rejected by CA policy. | Inspect the CSR text before submission and the final certificate after issuance; use sequential indexes and the correct type. |
| Self-signed certificate is reported untrusted | Self-signing provides no public trust chain by itself. | Use it only in a controlled test/private trust setup, or obtain a certificate from an appropriate CA for public clients. |
| Private key prompts or automation fails | The key is encrypted, or the command’s passphrase handling differs from the environment. | Choose an explicit encrypted-key workflow with secure secret delivery, or use an unencrypted key only where storage permissions and secret controls are appropriate. |
7. Reliability, renewal, and operational notes
Keep the SAN inventory aligned with how services are reached. DNS aliases, migration endpoints, load balancers, and direct-IP clients can make the actual identity set larger than the one people first think of. Record which service owns the certificate and how each name is validated, then repeat SAN inspection after every issuance or renewal. A successful CSR command only proves that OpenSSL produced a request; it does not prove that the CA approved it, that clients trust it, or that the deployed endpoint serves it.
Protect the private key with access controls appropriate to the server and automation that use it. Limit copies, avoid logging secret material, and plan a renewal process early enough to handle CA validation, deployment, and rollback. Certificate validity periods and CA procedures vary, so follow the issuer’s current requirements rather than hard-coding assumptions from an example.
Performance is rarely the deciding factor in certificate creation: these commands run locally and the key generation/CA issuance workflow is not a browser-rendering task. For reliability, the important checks are correct identities, correct key-to-certificate pairing, a valid chain, successful deployment, and renewal monitoring. There is no universal cost for a SAN certificate in this procedure; fees, validation steps, and issuance options depend on the chosen CA and certificate type. Verify current terms with the issuer.
8. Capture screenshots while validating a website
Certificate setup and visual page capture solve different problems. If you are documenting how a secured site renders across environments after configuring TLS, you can use a browser automation workflow or a screenshot API. ScreenshotNeo is a website screenshot API and MCP server; it takes a URL and returns an image or PDF. Its screenshot call does not issue, inspect, or validate certificates, so use OpenSSL and your CA for the SAN workflow above.
Or skip the browser setup:
For a screenshot of a reachable page, make one GET request. See the ScreenshotNeo API docs for request options.
curl -G "https://api.screenshotneo.com/v1/shot" -d access_key=YOUR_API_KEY --data-urlencode url=https://example.com -o shot.webpScreenshotNeo removes cookie banners, popups, and chat widgets before the shot. Bot checks, blank pages, and failed loads are never billed. Its MCP server lets AI agents such as Claude, Cursor, and other MCP clients take screenshots. The free plan includes 1,000 screenshots a month with no card; paid plans start at $5 for 3,000. Sign up free for 1,000 screenshots a month, no card required.
9. FAQ
Can one SAN certificate cover both a domain and an IP?
Yes, if the issuing CA supports and approves the requested identities. Put hostnames in DNS.n entries and IP literals in IP.n entries, then confirm both types in the issued certificate.
Does the Common Name replace SAN?
Do not rely on the Common Name to cover names omitted from SAN. Include the client-used names in SAN and verify the issued certificate.
Can I use a SAN CSR with any certificate authority?
The general CSR workflow is common, but CA interfaces, allowed identity types, validation, and extension policies differ. Follow the selected CA’s current instructions and inspect its certificate output.
Does a valid SAN prove the website is secure?
No. It establishes identity coverage within certificate validation. It does not assess the site’s application security, server configuration, or content.


