How to Scrape Leboncoin.fr in 2026
Leboncoin scraping requires written authorization. Learn the legal, privacy and technical workflow for an approved data integration in 2026.
Direct answer: You should not scrape Leboncoin.fr unless LBC France has given you written authorization that covers the exact data, rate, storage and reuse you plan. Leboncoin pages are publicly viewable, but its current terms prohibit automated retrieval, indexing and extraction or reuse of its databases without prior express authorization. A browser that can display a listing does not grant permission to build a crawler.
For an approved project, use an authorized feed, export or partner API supplied by LBC France whenever possible. Define a narrow data inventory, minimize personal data, respect robots.txt and technical objections, keep the authorization and policy versions on file, and build deletion and objection handling into the system. If you do not have written permission, stop at research and contact LBC France about an authorized integration.
What Leboncoin allows, and what it restricts
LBC France states in its Conditions générales d’utilisation that it is the producer of the Leboncoin service databases. The same terms restrict extracting, reproducing or reusing database contents and prohibit using a robot, spider, search application or other automated means to retrieve or index site content without prior express authorization. The restriction applies even when a page can be opened without logging in.
Leboncoin’s privacy policy (version 31 August 2026) describes names, email addresses, IP addresses and browsing data as personal data. It also describes automated processing used for fraud prevention and protection against robotized attacks. Treat selectors, internal endpoints and anti-bot responses as volatile implementation details, not as a stable public API.
CNIL’s guidance says that “Web scraping is not, in itself, prohibited under the GDPR.” That does not make every scrape lawful. The controller still needs a lawful basis, a defined purpose, data minimization, retention limits and safeguards. CNIL also says to respect a site’s objections expressed through terms, robots.txt or CAPTCHA, and its January 2026 guidance highlights database-producer rights and terms of use. See the CNIL web-scraping guidance before designing collection.
Before writing code: an authorization checklist
- Write the use case. State why you need the data, who will use it and what decision it supports.
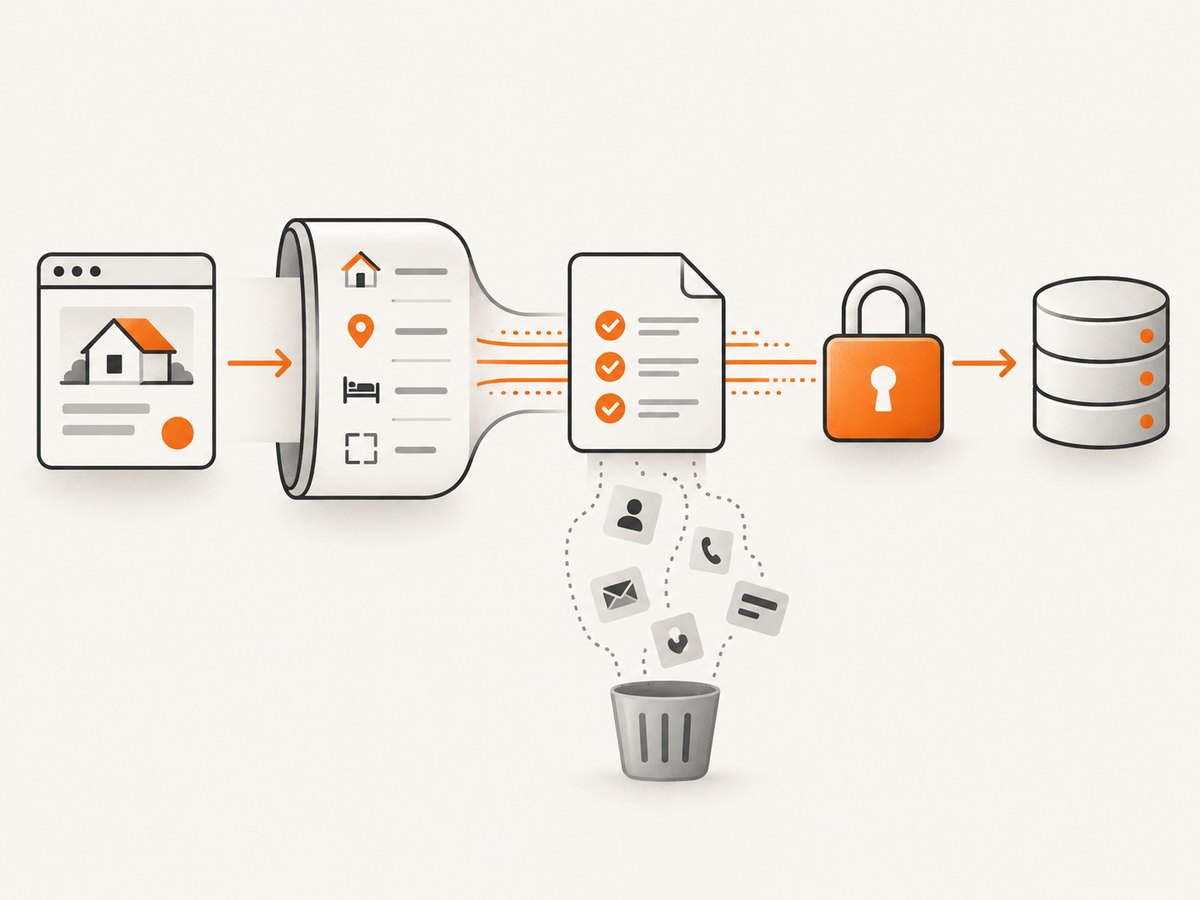
- List fields precisely. A minimal inventory might contain category, price, coarse location, posting date and listing URL. Mark every field as required or optional.
- Request written permission. Ask LBC France for an authorized feed, export or API. The agreement should identify permitted paths or datasets, geography, request limits, freshness, retention, redistribution and deletion obligations.
- Exclude unnecessary personal data. Do not collect message content, phone numbers, email addresses, precise addresses, seller profiles or images unless the authorization and documented purpose require them.
- Record objections. Keep a suppression list for URLs, sellers or categories that must not be collected, and honor robots.txt, CAPTCHA, login barriers and other explicit controls.
- Secure the result. Restrict access, encrypt transfers and storage, log provenance, and schedule deletion of records that are no longer necessary.
- Document decisions. Keep the signed permission, data inventory, lawful-basis analysis, policy versions, retention schedule and an incident/contact path.
Use an authorized machine interface
The official pages reviewed for this guide do not document a public self-serve scraping API, affiliate feed or export signup. Ask LBC France what licensed options are currently available. Once you receive an endpoint and credentials, prefer it over HTML parsing. An approved interface is easier to audit, rate-limit and shut down than a crawler coupled to changing page markup.
Minimal Python ingestion client
The following example is deliberately built for an endpoint you are authorized to call. It sends a narrow query, stores only an allow-list of fields and rejects records that contain unexpected personal-data fields. Replace the placeholder URL and authentication method with the details in your agreement.
import os
import requests
from datetime import datetime, timezone

FEED_URL = os.environ["LEBONCOIN_AUTHORIZED_FEED_URL"]
TOKEN = os.environ["LEBONCOIN_FEED_TOKEN"]

params = {
    "category": "bicycles",
    "updated_since": "2026-09-01T00:00:00Z",
    "limit": 100,
}
headers = {"Authorization": f"Bearer {TOKEN}", "Accept": "application/json"}
response = requests.get(FEED_URL, params=params, headers=headers, timeout=30)
response.raise_for_status()
payload = response.json()

allowed = {"id", "url", "category", "price", "location_area", "posted_at"}
records = []
for item in payload.get("items", []):
    clean = {key: item.get(key) for key in allowed if key in item}
    clean["source"] = "leboncoin-authorized-feed"
    clean["collected_at"] = datetime.now(timezone.utc).isoformat()
    records.append(clean)

print(f"Prepared {len(records)} minimized records")
# Write records only after applying your retention and access-control policy.
Equivalent cURL request
curl --fail-with-body --get "$LEBONCOIN_AUTHORIZED_FEED_URL" \
  -H "Authorization: Bearer $LEBONCOIN_FEED_TOKEN" \
  -H "Accept: application/json" \
  --data-urlencode "category=bicycles" \
  --data-urlencode "updated_since=2026-09-01T00:00:00Z" \
  --data-urlencode "limit=100"
Equivalent Node.js request
const feed = process.env.LEBONCOIN_AUTHORIZED_FEED_URL;
const token = process.env.LEBONCOIN_FEED_TOKEN;
const query = new URLSearchParams({
  category: 'bicycles',
  updated_since: '2026-09-01T00:00:00Z',
  limit: '100'
});

const res = await fetch(`${feed}?${query}`, {
  headers: {
    Authorization: `Bearer ${token}`,
    Accept: 'application/json'
  }
});
if (!res.ok) throw new Error(`Feed request failed: ${res.status}`);
const payload = await res.json();
const allowed = new Set(['id', 'url', 'category', 'price', 'location_area', 'posted_at']);
const records = (payload.items ?? []).map(item => {
  const clean = Object.fromEntries(
    Object.entries(item).filter(([key]) => allowed.has(key))
  );
  return { ...clean, source: 'leboncoin-authorized-feed', collected_at: new Date().toISOString() };
});
console.log(`Prepared ${records.length} minimized records`);
Pagination, updates and storage design
Follow the pagination and change-feed rules in your agreement. Use a server-provided cursor rather than guessing page numbers. Persist the cursor only after a batch has passed validation, then retry a failed batch with the same cursor. Make writes idempotent using the feed’s stable identifier and an upsert operation.
| Concern | Recommended practice |
|---|---|
| Freshness | Choose an interval in the contract; do not poll continuously “just in case.” |
| Duplicates | Use the authorized record ID as the primary key and retain source timestamps. |
| Deletion | Implement tombstones or a deletion job so removed records leave your database promptly. |
| Provenance | Store feed name, authorization scope, collection time and transformation version. |
| Personal data | Separate restricted fields, apply least-privilege access and define a short retention period. |
What not to do
- Do not rotate identities, proxies or accounts to evade limits.
- Do not solve or bypass CAPTCHA, bot checks, login barriers or access controls.
- Do not publish a selector recipe as a durable Leboncoin integration.
- Do not copy seller contact details or precise addresses “for later” without a documented necessity and authorization.
- Do not resell or republish listings unless the written agreement expressly permits it.
Performance, reliability and cost planning
For an approved feed, performance is mostly a contract and systems-design question. Batch within the permitted limit, use exponential backoff for transient 429 and 5xx responses, and cap concurrency below the agreed rate. Set a request timeout, record latency and status, and alert on sustained changes rather than retrying indefinitely.
Budget for the licensed data arrangement, engineering, storage, monitoring, privacy reviews and deletion workflows. The public pages reviewed do not establish a Leboncoin self-serve API price, quota or service-level commitment, so obtain those numbers from LBC France before committing to a forecast.
Reliability improves when your application can operate with stale data during a feed outage. Keep the last successful cursor, expose the age of the newest record to downstream users and fail closed when authorization expires. Never silently fall back to scraping the public site.
Or skip the browser setup
If your actual requirement is a visual record of a public Leboncoin page rather than a database of listings, ScreenshotNeo can capture the page through one API request. Read the ScreenshotNeo documentation for the complete option list and ensure your use still complies with Leboncoin’s terms.
curl -G "https://api.screenshotneo.com/v1/shot" -d access_key=YOUR_API_KEY --data-urlencode url=https://www.leboncoin.fr -o shot.webpimport requests
r = requests.get("https://api.screenshotneo.com/v1/shot", params={"access_key": "YOUR_API_KEY", "url": "https://www.leboncoin.fr"}, timeout=90)
open("shot.webp", "wb").write(r.content)const q = new URLSearchParams({ access_key: 'YOUR_API_KEY', url: 'https://www.leboncoin.fr' });
const res = await fetch(`https://api.screenshotneo.com/v1/shot?${q}`);ScreenshotNeo removes cookie and consent banners, newsletter popups and chat widgets before capture. Bot checks, blank pages, failed loads and cache hits are not billed, and response headers identify the page verdict and whether the request was billed. Its MCP server provides take_screenshot, get_page_info and capture_pdf for Claude, Cursor and other MCP clients. The Free plan includes 1,000 screenshots per month without a card; paid plans start at $5 for 3,000 shots. Create a free ScreenshotNeo account.
Troubleshooting an authorized integration
401 or 403 responses
Cause: expired credentials, an IP restriction or a request outside the written scope. Fix: verify the token, endpoint and allowed categories with LBC France. Do not respond by creating another account or bypassing the restriction.
429 rate-limit responses
Cause: concurrency or polling exceeds the contract. Fix: reduce workers, honor Retry-After, add exponential backoff and ask for a documented quota increase if needed.
Empty or incomplete batches
Cause: an invalid cursor, a filter that excludes records, or a feed freshness rule. Fix: log the exact parameters, validate the cursor transition and compare results with the feed’s documented semantics. Do not fill gaps by crawling HTML.
Schema changes
Cause: a version change or an undocumented field transformation. Fix: validate against a schema, quarantine unknown fields, alert on missing required fields and contact the feed owner before changing production mappings.
Privacy request or objection
Cause: a person asks for deletion, access or objection. Fix: locate records through your provenance key, stop further collection where required, apply the approved deletion process and document the decision.
FAQ
Can I scrape Leboncoin without logging in?
You may be able to view public pages without an account, but that does not authorize automated extraction. Obtain written permission first.
Is Leboncoin scraping legal in France?
There is no single yes-or-no answer. GDPR does not automatically prohibit scraping, while Leboncoin’s terms and database rights can prohibit the activity. Your purpose, lawful basis, data minimization and written authorization all matter.
Does Leboncoin have an API?
The official pages reviewed do not document a public self-serve scraping API or partner signup. Contact LBC France for current licensed options.
Can I reuse listings in my own database?
Only when your authorization and privacy analysis permit the specific fields, retention and reuse. Public visibility alone is not permission to copy or redistribute listings.
Can ScreenshotNeo replace a licensed data feed?
No. It produces screenshots or PDFs for visual capture. It does not grant permission to extract, store or redistribute Leboncoin data, and you remain responsible for complying with the site’s terms.
Final checklist
- Written LBC France authorization is stored and covers your exact fields and use.
- Your collection purpose, lawful basis, retention and deletion process are documented.
- Robots.txt, CAPTCHA, login barriers and other objections are respected.
- Your client uses the authorized interface, bounded retries and idempotent writes.
- Personal data is minimized, secured and excluded when unnecessary.
- Downstream users can see provenance and data age.


