DNS Record Lookup: Check Domain DNS Records
Learn how to check A, AAAA, MX, TXT, CNAME, NS and other DNS records with browser tools, dig, Python and Node.js.
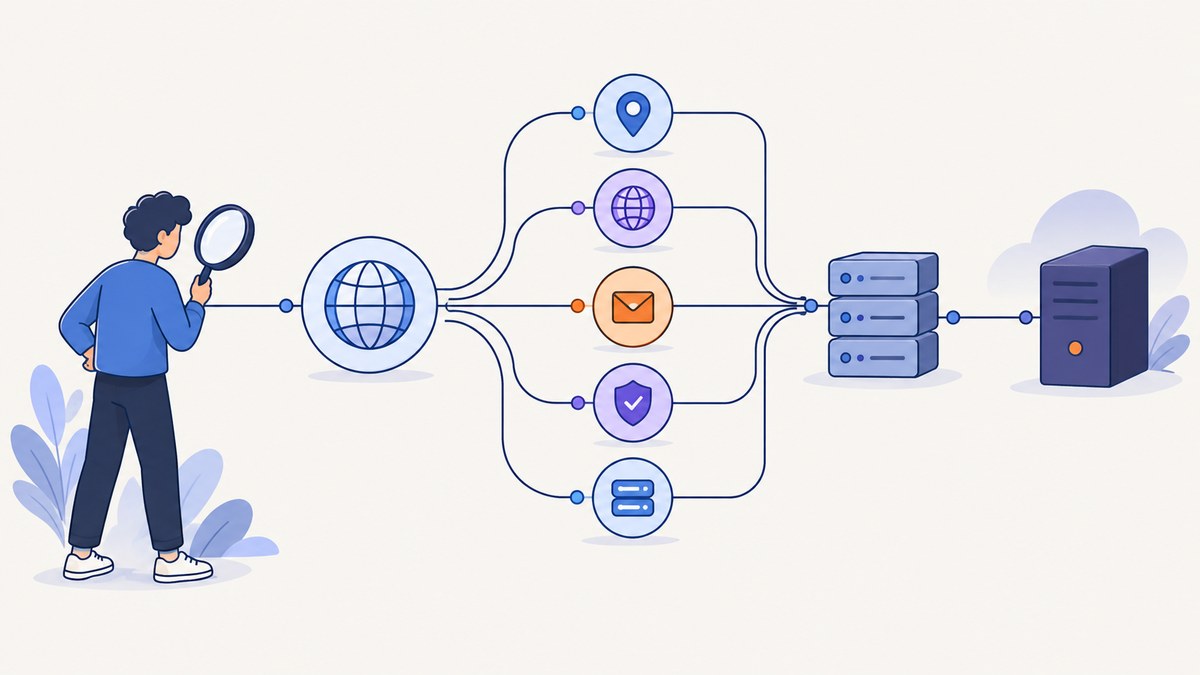
Direct answer: to check a domain’s DNS records, query the specific record type you need with dig, a browser lookup tool, Python, or Node.js. For example, run dig example.com A for an IPv4 address, dig example.com MX for mail routing, or dig example.com TXT for verification and email-authentication data. Record answers come from the resolver you query at that moment; a cached answer may lag behind the authoritative zone.
What a DNS lookup actually tells you
DNS (Domain Name System) lookup asks a resolver for a domain name and a record type. The response normally contains the record name, type, value, TTL and sometimes additional records. It is a snapshot of what that resolver can currently answer, not a guaranteed export of every record configured at the DNS provider.
A DNS record has four useful parts:
- Name: the domain or host label, such as
example.comorwww.example.com. - Type: how to interpret the value.
- Content: the address, hostname, mail server, text or service data.
- TTL: how many seconds a recursive resolver may cache the answer before asking again.
Cloudflare’s DNS record reference documents the common types and their fields. Its DNS records overview explains how records are managed and why TTL affects propagation.
Choose the record type that answers your question
| Type | What it is for | Example command |
|---|---|---|
| A | Maps a name to an IPv4 address. | dig example.com A |
| AAAA | Maps a name to an IPv6 address. | dig example.com AAAA |
| CNAME | Points a name to another canonical hostname. | dig www.example.com CNAME |
| MX | Lists mail-exchange destinations and priorities. | dig example.com MX |
| NS | Identifies the authoritative name servers for a zone. | dig example.com NS |
| TXT | Stores text, commonly verification and email-authentication data. | dig example.com TXT |
| SOA | Describes zone authority, serial and timing fields. | dig example.com SOA |
| SRV | Publishes a service hostname and port. | dig _sip._tcp.example.com SRV |
SPF is commonly searched as a separate type, but Google Cloud’s record overview notes that the SPF record type is deprecated. Modern SPF policy is published in a TXT record beginning with v=spf1.

Fast browser lookup
- Open Google Public DNS lookup or the Dig Web Interface. Cloudflare lists both as useful third-party lookup tools.
- Enter the domain without a path, such as
example.com. - Select the record type, or request the common record set if the tool supports it.
- Record the resolver, answer, TTL and timestamp. Keep those details if you are diagnosing a DNS change.
Browser tools are convenient for a quick inspection, but they hide some resolver details. Use dig when you need repeatable output, resolver selection, DNSSEC flags or authoritative checks.
Use dig from a terminal
On Debian or Ubuntu, install it with sudo apt install dnsutils. On macOS, it is included with the system DNS tools. Windows users can install BIND utilities or use PowerShell’s Resolve-DnsName.
dig example.com A
dig example.com AAAA
dig example.com CNAME
dig example.com MX
dig example.com NS
dig example.com TXT
dig example.com SOA
dig _sip._tcp.example.com SRV
The default output includes the server queried, status, answer section and TTL. For concise scripts, use the short form:
dig +short example.com A
dig +short example.com MX
dig +short example.com TXT
Ask a particular recursive resolver to compare caches:
dig @1.1.1.1 example.com A
dig @8.8.8.8 example.com A
Find the authoritative name servers, then query one directly:
dig +short example.com NS
dig @ns1.example-dns.com example.com A
Replace the name server in the second command with an actual NS returned by the first. An authoritative response shows the zone’s published data; a recursive response may still be serving an older cached value.
Useful dig flags and DNS details
| Flag | Use |
|---|---|
+short |
Print only values, useful in shell pipelines. |
+noall +answer |
Show only the answer section with name, TTL, class, type and value. |
+trace |
Walk from root servers toward the authoritative answer to investigate delegation. |
+dnssec |
Request DNSSEC-related data when supported. |
-x 203.0.113.10 |
Perform a reverse lookup (PTR) for an IP address. |
+tcp |
Retry over TCP when UDP responses are truncated or filtered. |
DNS names are case-insensitive. A trailing dot in a fully qualified name, such as example.com., is equivalent to the usual spelling. A CNAME can lead to another lookup, so seeing a CNAME without its final A or AAAA value is not necessarily an error.
Check records with Python
The following standard-library script calls the local dig command and returns concise records. It exits nonzero when the lookup fails, making it suitable for a deployment check.
#!/usr/bin/env python3
import argparse
import shutil
import subprocess
import sys

parser = argparse.ArgumentParser()
parser.add_argument("domain")
parser.add_argument("record_type", nargs="?", default="A")
parser.add_argument("--server", help="DNS resolver or authoritative server")
args = parser.parse_args()

if shutil.which("dig") is None:
    sys.exit("dig is required; install dnsutils or bind-utils")

command = ["dig", "+noall", "+answer"]
if args.server:
    command.append("@" + args.server)
command += [args.domain, args.record_type]
result = subprocess.run(command, text=True, capture_output=True, timeout=10)
if result.returncode:
    sys.exit(result.stderr.strip() or "DNS query failed")
print(result.stdout, end="")
Run it as python3 dns_check.py example.com MX or compare a public resolver with an authoritative server using --server 1.1.1.1.
Check records with Node.js
Node’s built-in dns/promises module performs typed lookups without an external package. This example prints the most useful common types.
import dns from "node:dns/promises";

const domain = process.argv[2] ?? "example.com";
const resolver = new dns.Resolver();
// Optional: query a specific recursive resolver.
// resolver.setServers(["1.1.1.1"]);

try {
  const [a, aaaa, mx, ns, txt] = await Promise.all([
    resolver.resolve4(domain),
    resolver.resolve6(domain).catch(() => []),
    resolver.resolveMx(domain),
    resolver.resolveNs(domain),
    resolver.resolveTxt(domain),
  ]);
  console.log(JSON.stringify({ domain, A: a, AAAA: aaaa, MX: mx, NS: ns, TXT: txt }, null, 2));
} catch (error) {
  console.error(`${error.code ?? "DNS_ERROR"}: ${error.message}`);
  process.exitCode = 1;
}
Save as dns-check.mjs and run node dns-check.mjs example.com. Use resolver.resolveCname(domain), resolveSoa or resolveSrv when you need those types.
Interpret changes and conflicting answers
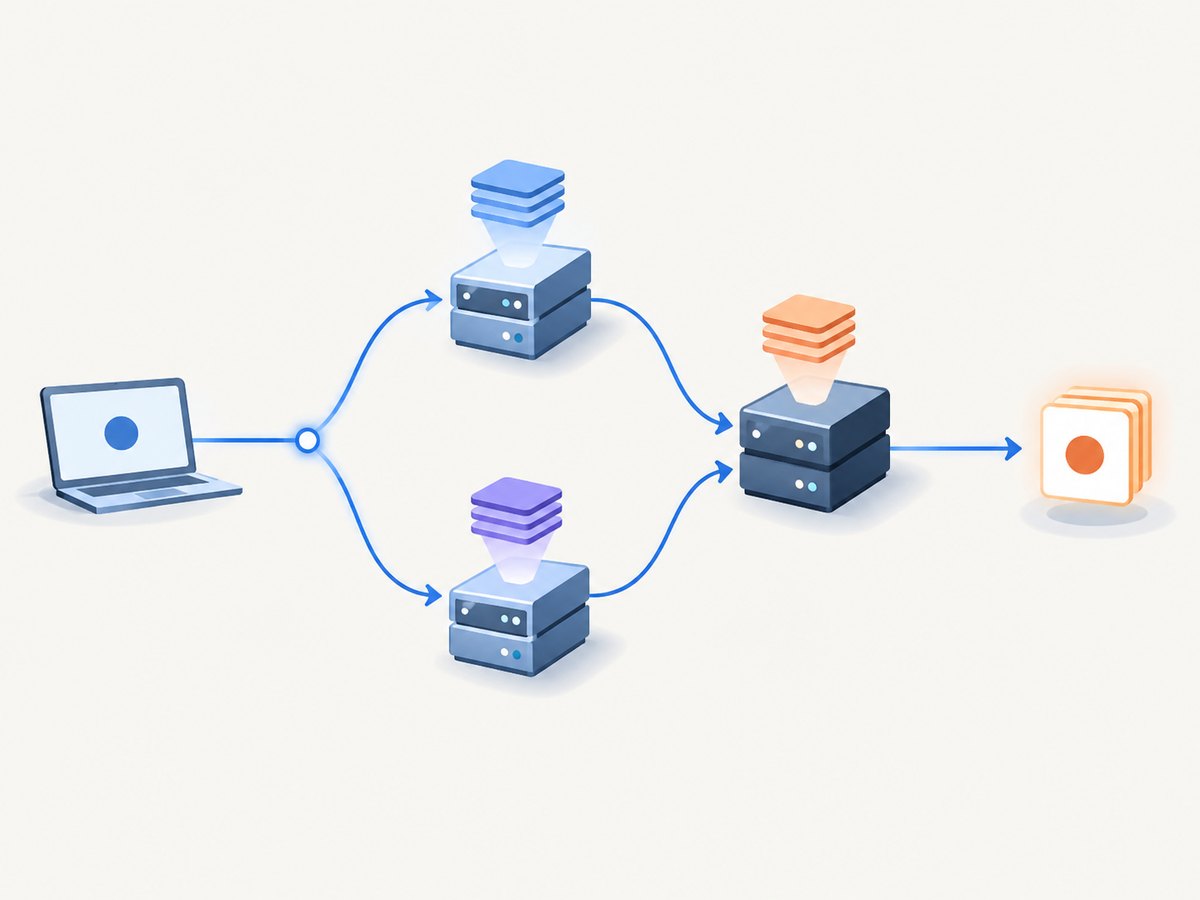
After editing a record, compare four things: the exact name, the record type, the resolver, and the TTL. A recursive resolver can legally return the previous value until its cached TTL expires. Query two recursive resolvers and then an authoritative server:
dig @1.1.1.1 example.com TXT +noall +answer
dig @8.8.8.8 example.com TXT +noall +answer
dig +short example.com NS
# Query one returned authoritative server:
dig @AUTHORITATIVE_SERVER example.com TXT +noall +answer
If the authoritative answer is correct while a recursive answer is old, wait for the cached TTL. If the authoritative answer is wrong, the edit was made in a different DNS zone, the name is misspelled, or the change was not saved. A lookup never changes DNS; edits require access to the DNS management service responsible for the delegated zone.
Troubleshooting common DNS lookup errors
| Symptom | Likely cause | Fix |
|---|---|---|
NXDOMAIN |
The queried name does not exist in the zone, or delegation is wrong. | Check spelling, query the parent NS records and confirm the zone is delegated. |
NOERROR with no answer |
The name exists but has no record of the requested type. | Query the intended type; inspect CNAME or the zone’s authoritative data. |
| Old value after an edit | A recursive cache still holds the previous answer. | Read the returned TTL, compare another resolver and query an authoritative server. |
Timeout or SERVFAIL |
Resolver failure, DNSSEC issue, unreachable authoritative server or transient network problem. | Retry, compare resolvers, use +trace, and inspect DNSSEC or delegation at the provider. |
| Missing TXT text | Long TXT data is split into quoted chunks, or multiple TXT records exist. | Read all chunks and concatenate them according to the application’s rules; do not assume the first line is the only value. |
| Expected CNAME is absent at the apex | Many DNS providers do not allow a conventional CNAME at a zone apex. | Check the provider’s alias/flattening feature or query the record actually published. |
Performance, reliability and cost
A single typed lookup is lightweight, but a script that checks many domains should limit concurrency, set a timeout and cache results for no longer than the returned TTL unless you have a deliberate monitoring policy. Querying several resolvers improves diagnosis but increases network requests. For reliable automation, log the domain, type, resolver, status, values, TTL and timestamp; alert only after repeated failures to avoid treating a transient resolver problem as a zone outage.
Local dig, Python and Node DNS calls have no per-query software fee. Public recursive resolvers may impose operational policies, and managed DNS providers charge according to their own plans; lookup tooling does not grant permission to edit records. Your main operational cost is the monitoring volume and any DNS hosting service you already use.
Or skip the browser setup
If your workflow needs a screenshot of a DNS lookup page, ScreenshotNeo can capture the result with one GET request. See the ScreenshotNeo API documentation for all parameters.
curl -G "https://api.screenshotneo.com/v1/shot" -d access_key=YOUR_API_KEY --data-urlencode url=https://dns.google/query?name=example.com&type=A -o shot.webpimport requests
r = requests.get("https://api.screenshotneo.com/v1/shot", params={"access_key": "YOUR_API_KEY", "url": "https://dns.google/query?name=example.com&type=A"}, timeout=90)
open("shot.webp", "wb").write(r.content)const q = new URLSearchParams({ access_key: 'YOUR_API_KEY', url: 'https://dns.google/query?name=example.com&type=A' });
const res = await fetch(`https://api.screenshotneo.com/v1/shot?${q}`);Cookie banners, newsletter popups and chat widgets are removed before the shot. Bot checks, blank pages and failed loads are never billed, and the response identifies the page verdict and billing status in headers. An MCP server lets AI agents take screenshots, inspect page information and capture PDFs. You get 1,000 screenshots a month free with no card; paid plans start at $5 for 3,000. Create a free ScreenshotNeo account.
FAQ
Does a DNS lookup show every record?
No. It shows the answer for the name and type requested by a particular resolver. Query each relevant type and check the authoritative server when completeness matters.
How long does DNS propagation take?
There is no single fixed time. Recursive resolvers can cache an answer for its TTL, so the old value may remain visible until that cache expires.
Can I edit a record with dig?
No. dig only queries DNS. Make changes in the DNS management service for the authoritative zone.
Why do MX records include numbers?
The number is the preference value. Mail systems generally try the lowest preference first, then fall back to higher values.
Should SPF be queried as TXT?
Yes. SPF policy is normally stored in TXT data beginning with v=spf1; the SPF record type is deprecated.