What Is a Payload? Network Packets, HTTP APIs, and Malware
A payload is the useful data carried by a packet or message. Learn how payloads work in networks, HTTP APIs, JSON, and cybersecurity.
Short answer: a payload is the useful data carried inside a larger message or transmission unit. The surrounding structure—such as a packet header or HTTP headers—contains information needed to deliver, parse, or interpret that data. A payload can be bytes, text, JSON, an image, HTML, or executable code. The word does not describe one particular format.
Meaning depends on context. In networking, the payload is the data carried by a packet. In HTTP and APIs, it is the representation transferred in a request or response, with meaning defined by the HTTP method and status. In cybersecurity, a “malware payload” is the code or function delivered by an attack. These uses are related, but they should not be treated as synonyms.
Payload versus header
A protocol data unit usually combines control information with data. The header helps a system route, validate, or process the unit; the payload is what the sender wants the receiver to carry or consume.
| Part | Typical purpose | Example |
|---|---|---|
| Header | Addressing, length, encoding, routing, or metadata | Source and destination IP addresses |
| Payload | Application or user data being transported | Part of an image, a JSON object, or a web page |
| Trailer (when present) | Integrity checks or framing information | A checksum used by a link-layer protocol |
“Payload” is relative to the layer being discussed. An HTTP response is carried inside a TCP stream, which is carried inside IP packets. The HTTP response has an HTTP payload; each IP packet has an IP payload that includes part of that TCP stream. A large file can therefore be divided across many packets, and each packet carries only a fragment.
What is a payload in a network packet?
In a network packet, the payload is the carried data after the protocol header. An IP header contains addressing and control fields so routers and hosts can forward the packet. The IP payload commonly contains a transport segment such as TCP or UDP data, which in turn may contain an application message.
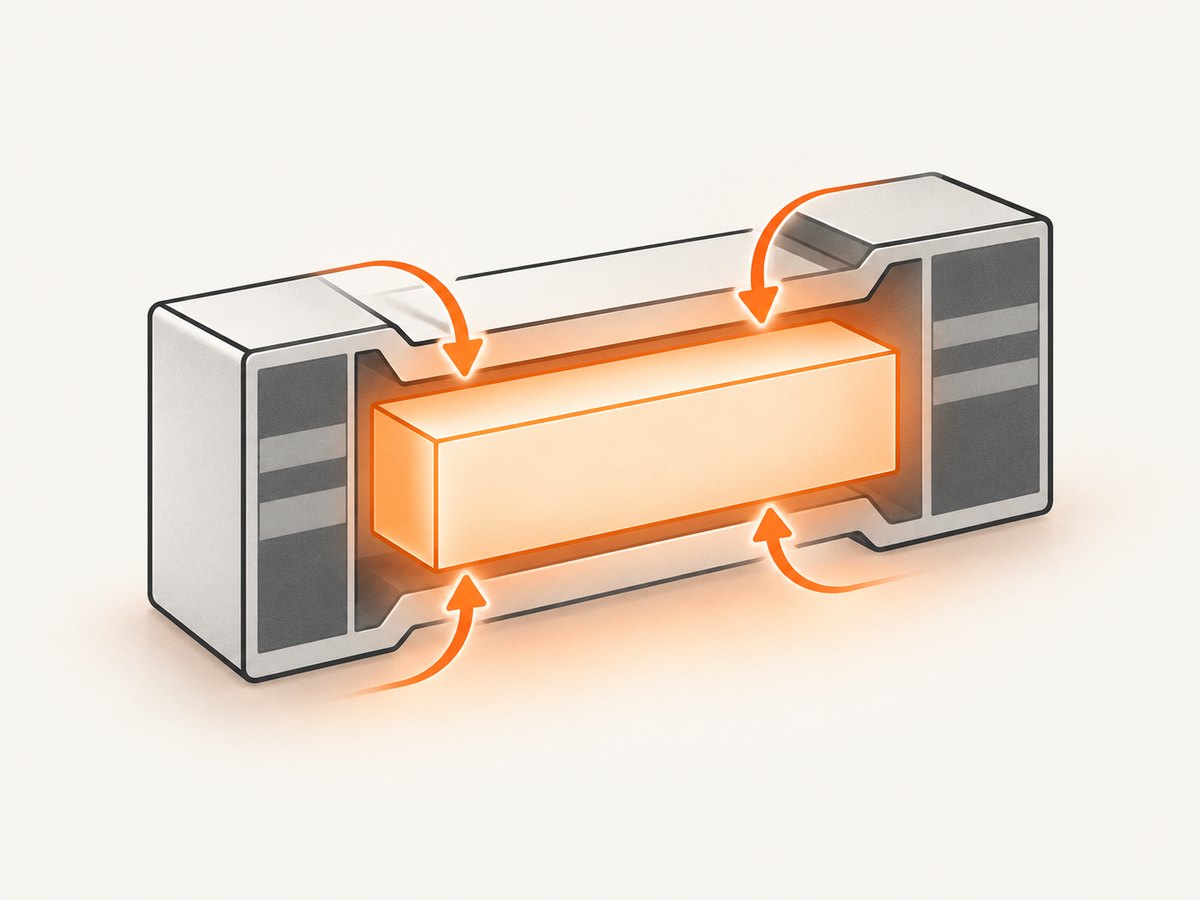
Packet captures show this layering. If you inspect an HTTPS connection, you may see an IP packet carrying a TCP segment carrying encrypted TLS records. The application payload is protected by encryption, so a packet analyzer can identify sizes and endpoints but cannot read the HTTP content without the appropriate keys.
- Read the packet’s protocol field to identify the next layer.
- Parse the header length to find where payload bytes begin.
- Use the next protocol’s parser to interpret those bytes.
- Reassemble fragments or stream segments before interpreting a complete application message.
Do not assume one packet equals one request. TCP is a byte stream, so a request can span packets, and several small messages can share one packet.
What is a payload in HTTP?
HTTP uses “payload” as a standards term for a complete or partial representation transferred in a message. RFC 7231, Section 3.3, states that some HTTP messages transfer a representation as the message payload and that “the purpose of a payload in a request is defined by the method semantics.” See the RFC 7231 payload semantics.
In practical API work, developers often call the request body or response body the payload. That shorthand is useful, but the body and payload are not always identical concepts: framing and transfer rules can exist even when no application data is present.
Request payloads by method
| Method | Common payload meaning | Typical format |
|---|---|---|
| POST | Information for the target resource to process, such as a new record or command | JSON, form data, multipart upload |
| PUT | The desired representation of a resource at a known URL | JSON or binary representation |
| PATCH | A partial change or patch document | JSON Merge Patch or JSON Patch |
| DELETE | Usually no payload; any body has application-specific meaning | Occasionally JSON |
| GET | Query parameters normally carry input. RFC 7231 defines no general semantics for a GET payload, and implementations may reject it | Prefer the URL query string |
Response payloads
A response payload is interpreted together with the request method and status code. A 200 response to GET commonly contains the requested representation. A 201 response to POST may contain the newly created resource. A 204 response intentionally has no response content. The Content-Type header identifies the media type, while headers such as Content-Length or Transfer-Encoding describe framing or representation metadata. MDN provides an accessible overview of HTTP headers.
Does payload mean JSON?
No. JSON is one possible encoding. Payload describes a message’s role, not its syntax. Valid payloads include:
application/jsoncontaining an object or arrayapplication/x-www-form-urlencodedform fieldsmultipart/form-datawith files and fields- XML, CSV, plain text, HTML, images, video, compressed archives, or arbitrary binary bytes
An AWS Partner Central CRM guide calls a structured JSON object exchanged in that particular workflow a payload. That is a service-specific definition, not a universal requirement that all payloads be JSON. Always check the API’s documented media type, schema, required fields, and size limits.
Example JSON request
curl -X POST https://api.example.test/users \
  -H 'Content-Type: application/json' \
  -d '{"name":"Ada","role":"admin"}'
Here the JSON object is the payload. The Content-Type header tells the server how to parse it. A missing or incorrect header can produce a 415 Unsupported Media Type response even when the JSON itself is valid.
What is a payload in cybersecurity?
Security writing uses “payload” in two ways. The neutral networking meaning still applies to every transmitted message. Separately, a malware payload is the code or behavior an attacker delivers after exploiting a vulnerability or gaining access. TechTarget uses this distinction in its explanation of payload terminology.
A phishing document may contain a downloader; the downloader fetches a second-stage payload; that stage may encrypt files or collect credentials. Calling the delivered code a payload describes its role in the attack chain—it does not mean that every network payload is malicious.
How to design and validate API payloads
- Choose the media type. Send the format the endpoint documents, usually with an explicit
Content-Type. - Validate before sending. Check required fields, types, enum values, string lengths, and nested objects against the schema.
- Separate data from credentials. Put API keys in an authorization header or secret store, never inside user-controlled payload fields.
- Keep retries safe. Use an idempotency key for operations that create resources when the API supports it. A timeout does not prove the server failed.
- Log safely. Record status, request ID, and a redacted shape of the payload. Avoid passwords, tokens, and personal data.
Payload edge cases
- Empty body: An empty payload is different from JSON
null, an empty object{}, and an empty array[]. Servers may validate them differently. - Encoding: Confirm UTF-8 expectations. Invalid byte sequences can fail before application validation.
- Compression:
Content-Encoding: gzipchanges how bytes are transferred; the decoded representation still needs the correct media type. - Size limits: Gateways may reject large payloads with 413. Upload large files directly to object storage when supported.
- Partial updates: In PATCH, distinguish an omitted field (leave unchanged) from an explicit null (clear it).
- Unknown fields: Some APIs ignore them, while strict schemas reject them. Follow the endpoint’s documented behavior.
Debugging payload errors
| Symptom | Likely cause | Fix |
|---|---|---|
| 400 Bad Request | Malformed syntax or failed validation | Print the exact bytes sent, validate against the schema, and inspect the server’s error details. |
| 401 or 403 | Missing, expired, or insufficient credentials | Check the authorization header, scopes, and clock skew; do not put secrets in the payload. |
| 415 Unsupported Media Type | Wrong or missing Content-Type | Set the documented media type and encode the body accordingly. |
| 413 Payload Too Large | Body exceeds a proxy or service limit | Compress, paginate, resize, or use a multipart/direct-upload flow. |
| 422 Unprocessable Content | Syntax is valid but semantic validation failed | Correct field values, formats, ranges, or relationships. |
| Timeout after a write | Network failure after the server may have accepted the payload | Use an idempotency key, query the resource, then retry according to the API policy. |
Performance, reliability, and cost considerations
Payload size affects transfer time, memory use, parsing cost, and sometimes billing. Send only fields the endpoint needs, paginate collections, and compress repetitive JSON when the server supports it. For high-throughput clients, reuse connections and stream large downloads instead of buffering them in memory.
Reliability depends on more than payload validity. Set connect and read timeouts, classify retries by status code, use exponential backoff with jitter, and preserve correlation IDs. Never blindly retry a non-idempotent POST unless the API documents safe retry behavior. Validate responses as carefully as requests; a 200 status does not guarantee every field has the expected type.
Inspecting payloads with a screenshot API
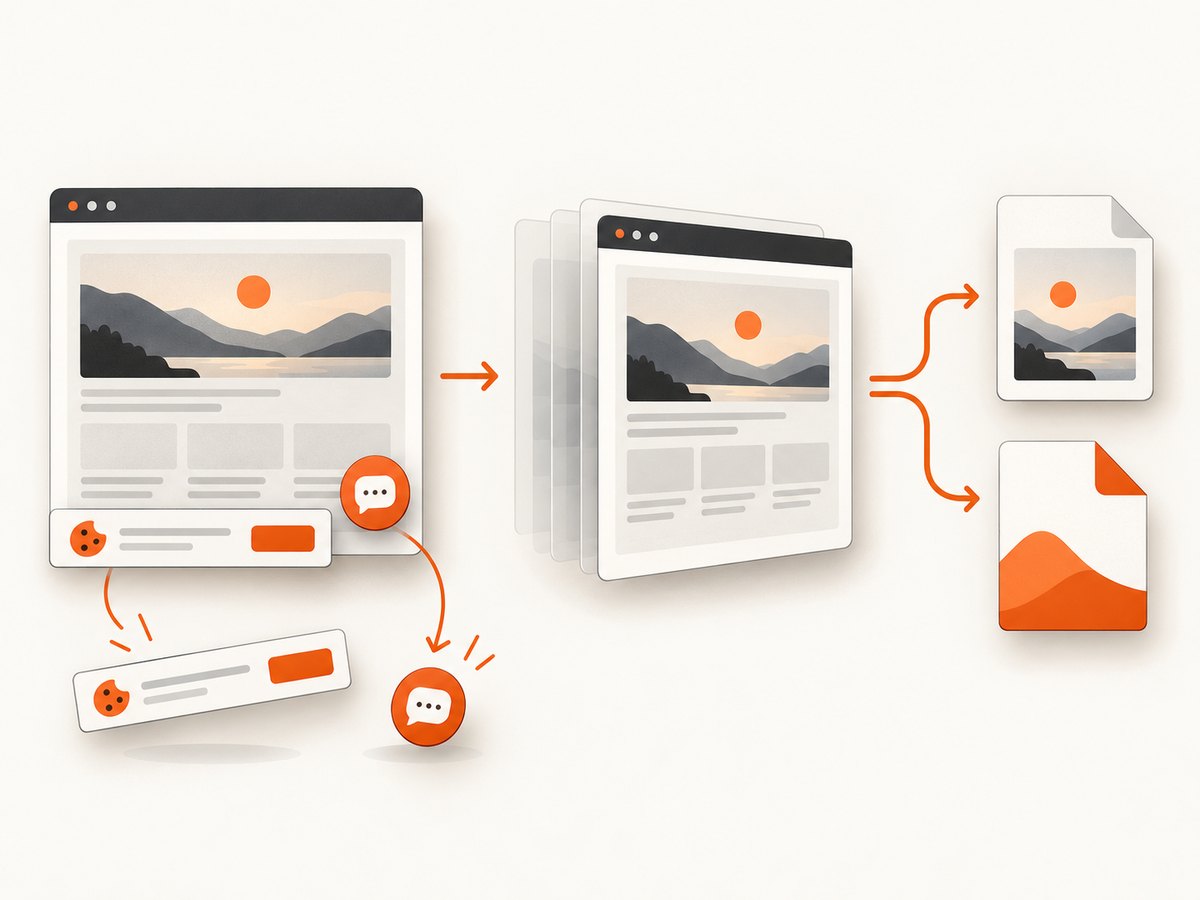
When documenting an API or debugging a web workflow, a screenshot can capture the rendered result after the request completes. You can build this yourself with a headless browser: launch Chromium, navigate to a URL, wait for network idle or a selector, apply cookies and headers, then save a PNG or PDF. Browser setup adds version management, sandbox configuration, consent banners, popups, retries, and operational cost.
Or skip the browser setup
ScreenshotNeo provides a website screenshot API and MCP server. One GET request returns PNG, JPEG, WebP, or PDF. Cookie and consent banners are accepted and 60+ known consent platforms, newsletter popups, and chat widgets are removed before capture; each step can be disabled. Bot checks, blank pages, timeouts, failed loads, and cache hits are not billed, and the response includes X-Page-Verdict and X-Billed headers. Its MCP server exposes take_screenshot, get_page_info, and capture_pdf for Claude, Cursor, and other MCP clients.
See the ScreenshotNeo API documentation for all options, including full-page and element capture, device presets, retina scale, dark mode, custom CSS and JavaScript, clicks, waits, blocked resources, headers, cookies, geolocation, PDF settings, resizing, caching, signed links, async jobs, webhooks, bulk capture, and usage reporting.
cURL
curl -G "https://api.screenshotneo.com/v1/shot" -d access_key=YOUR_API_KEY --data-urlencode url=https://stripe.com -o shot.webpPython
import requests
r = requests.get("https://api.screenshotneo.com/v1/shot", params={"access_key": "YOUR_API_KEY", "url": "https://stripe.com"}, timeout=90)
r.raise_for_status()
open("shot.webp", "wb").write(r.content)
Node.js
const q = new URLSearchParams({ access_key: 'YOUR_API_KEY', url: 'https://stripe.com' });
const res = await fetch(`https://api.screenshotneo.com/v1/shot?${q}`);
if (!res.ok) throw new Error(`${res.status} ${await res.text()}`);
const fs = await import('node:fs/promises');
await fs.writeFile('shot.webp', Buffer.from(await res.arrayBuffer()));
Plans include 1,000 shots per month free with no card; paid plans start at $5 for 3,000 shots, and every feature is available on every plan. Create a free ScreenshotNeo account to get started.
Payload FAQ
Is a payload the same as a message body?
Often in application documentation, yes. In formal protocol language, payload semantics and message framing are related but distinct, so consult the protocol specification.
Can a GET request have a payload?
Some clients can send one, but RFC 7231 defines no general semantics for it and servers may reject it. Use query parameters unless the API explicitly documents a GET body.
Is an API key a payload?
Usually it is authentication metadata in a header or query parameter. It becomes payload data only if the application intentionally places it in the request body.
How do I know what a payload contains?
Check the media type, schema, and method documentation, then inspect a redacted request or response with a proxy or API client. Do not log secrets or personal data.


